
Kick-start your app creation
Whether you’re a beginner or a pro, Dynatrace Developer has the tools and support you need to create incredible apps with minimal effort.
Go to Dynatrace Developer
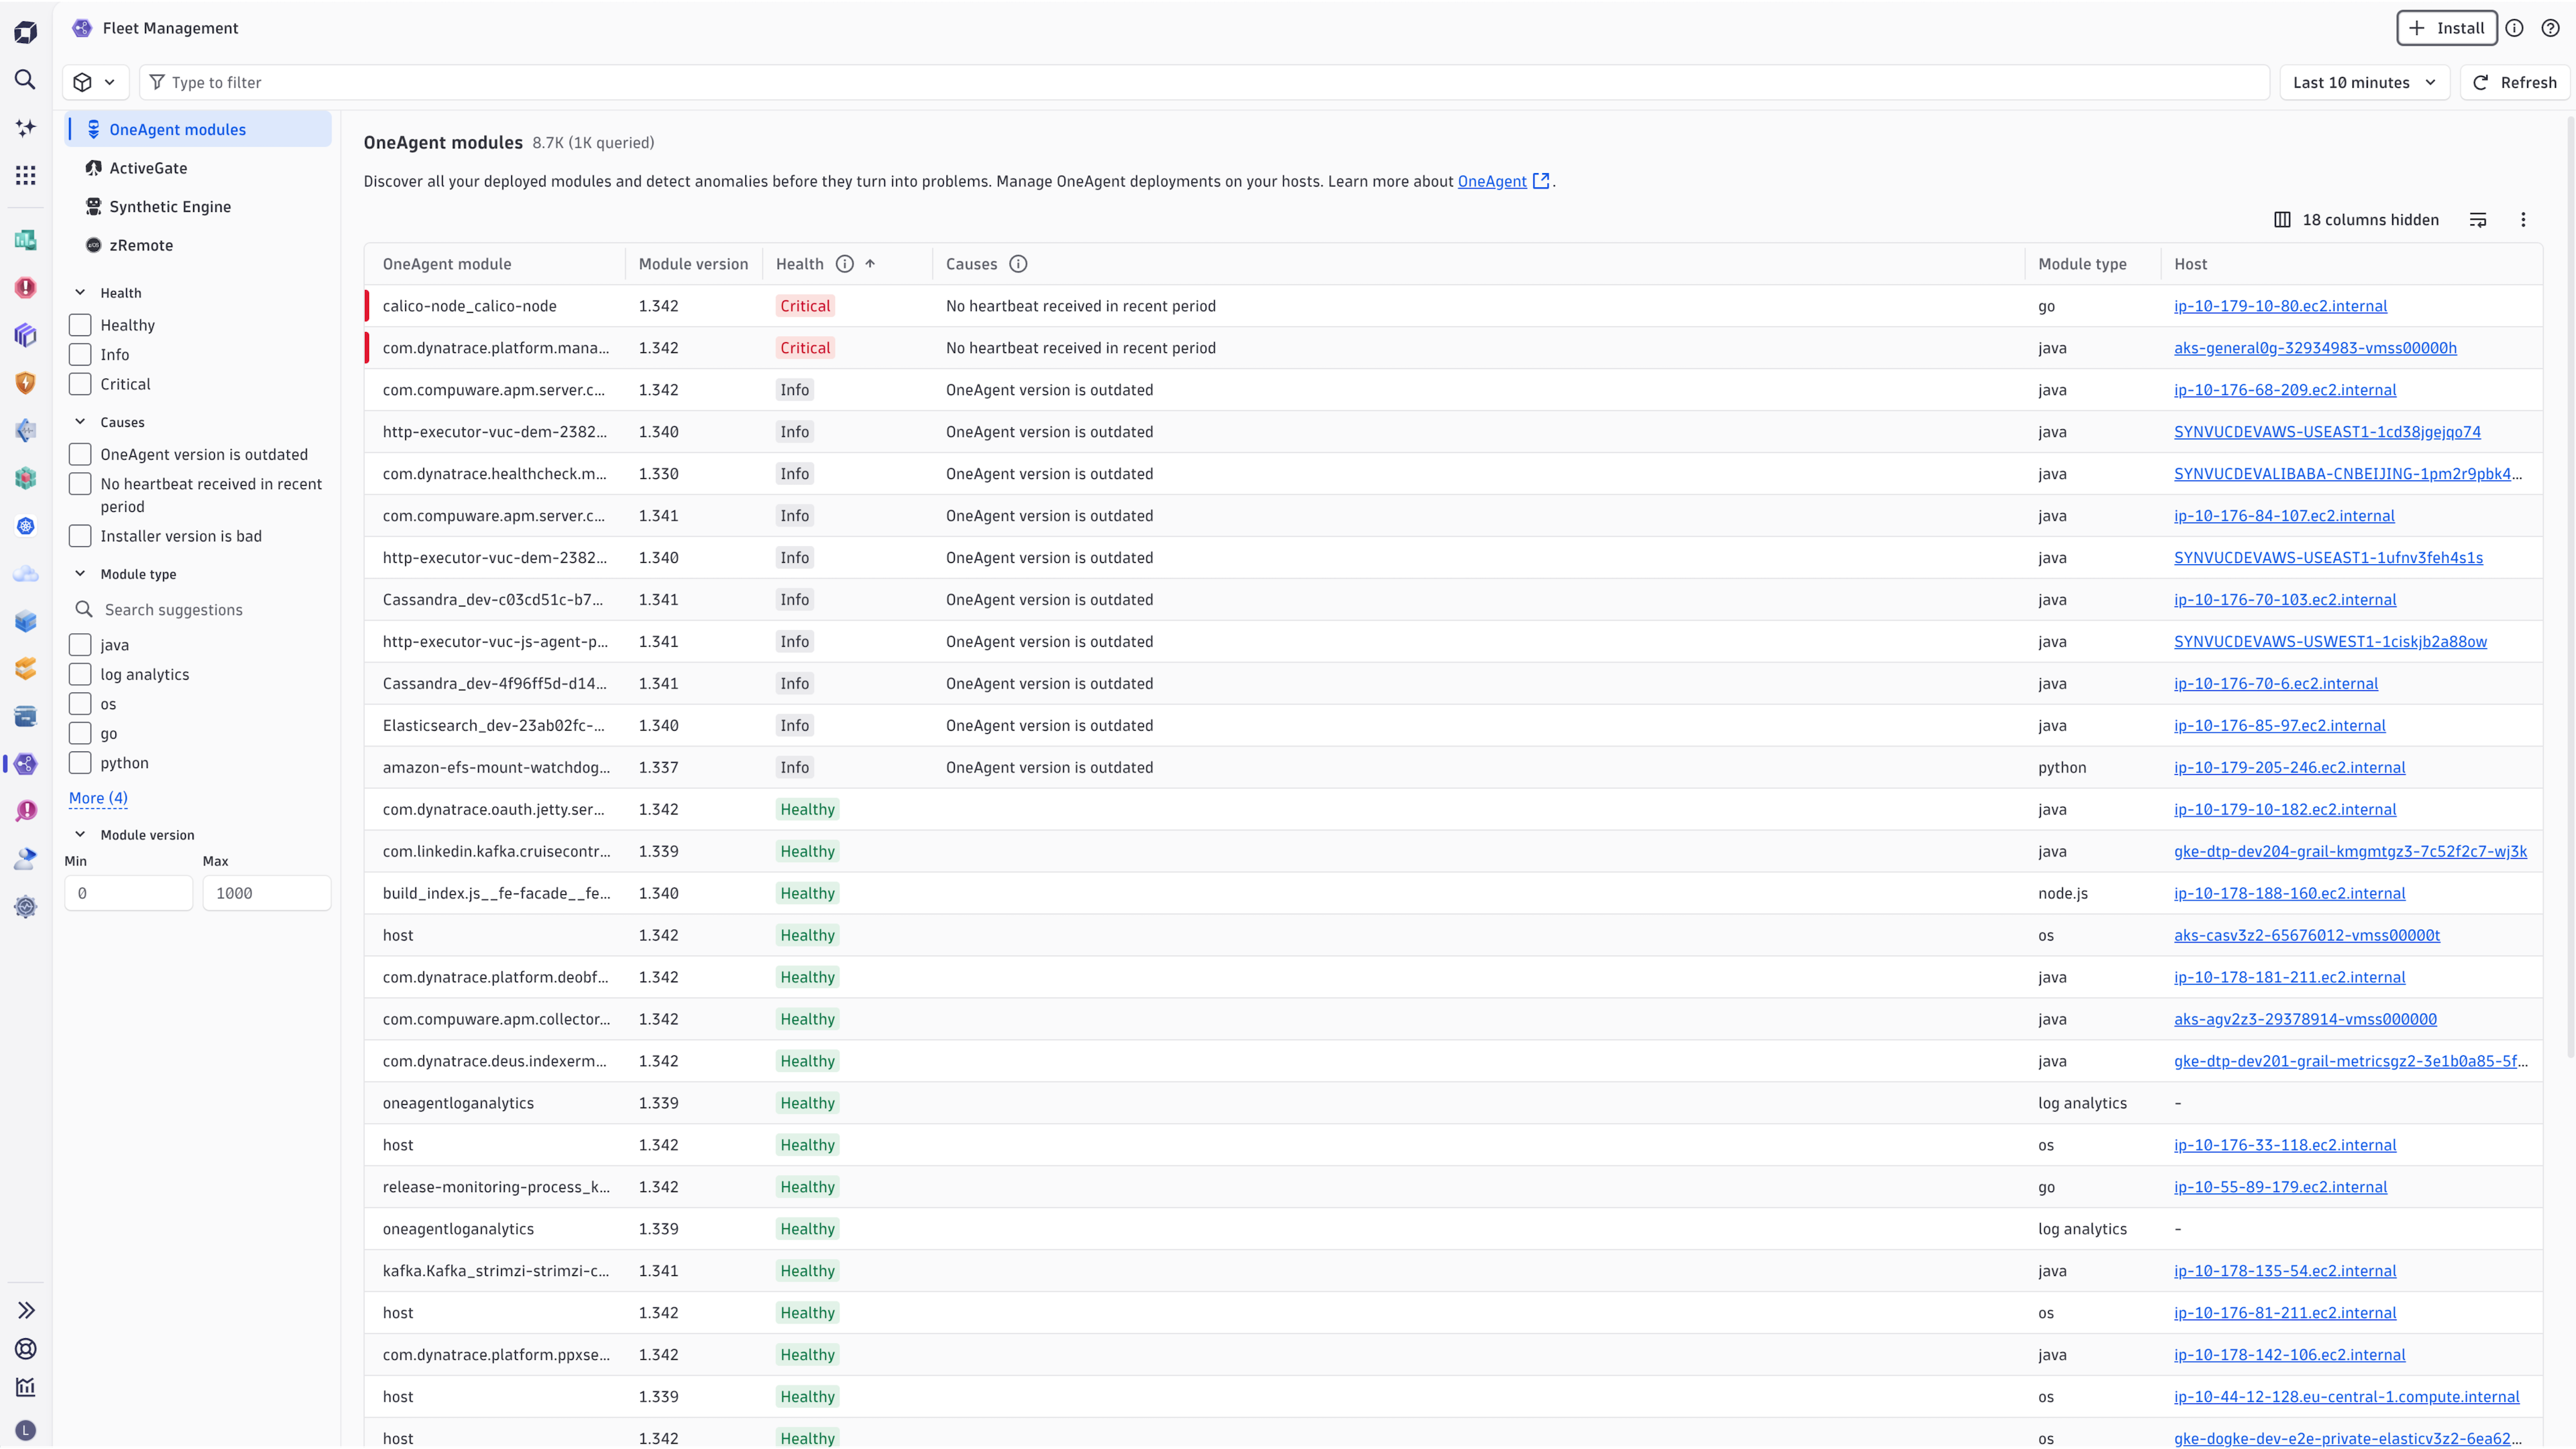
 Fleet Management
Monitor and manage deployed OneAgent and ActiveGate: health, install, updates.
AppFleet Management is the central place to monitor, manage, and automate the components and integrations that collect telemetry for your Dynatrace environment. It gives deployment and infrastructure admins everything they need to keep their fleet healthy and up to date at scale. With Fleet Management, you can:
Instant overview of the entire fleet. Review your fleet inventory, health issues, and version distribution at a glance. Recommended actions are prioritized, so you know what to address first.
Easier lifecycle management of fleet components. Manage updates centrally, reduce upgrade friction, and stay on a target version.
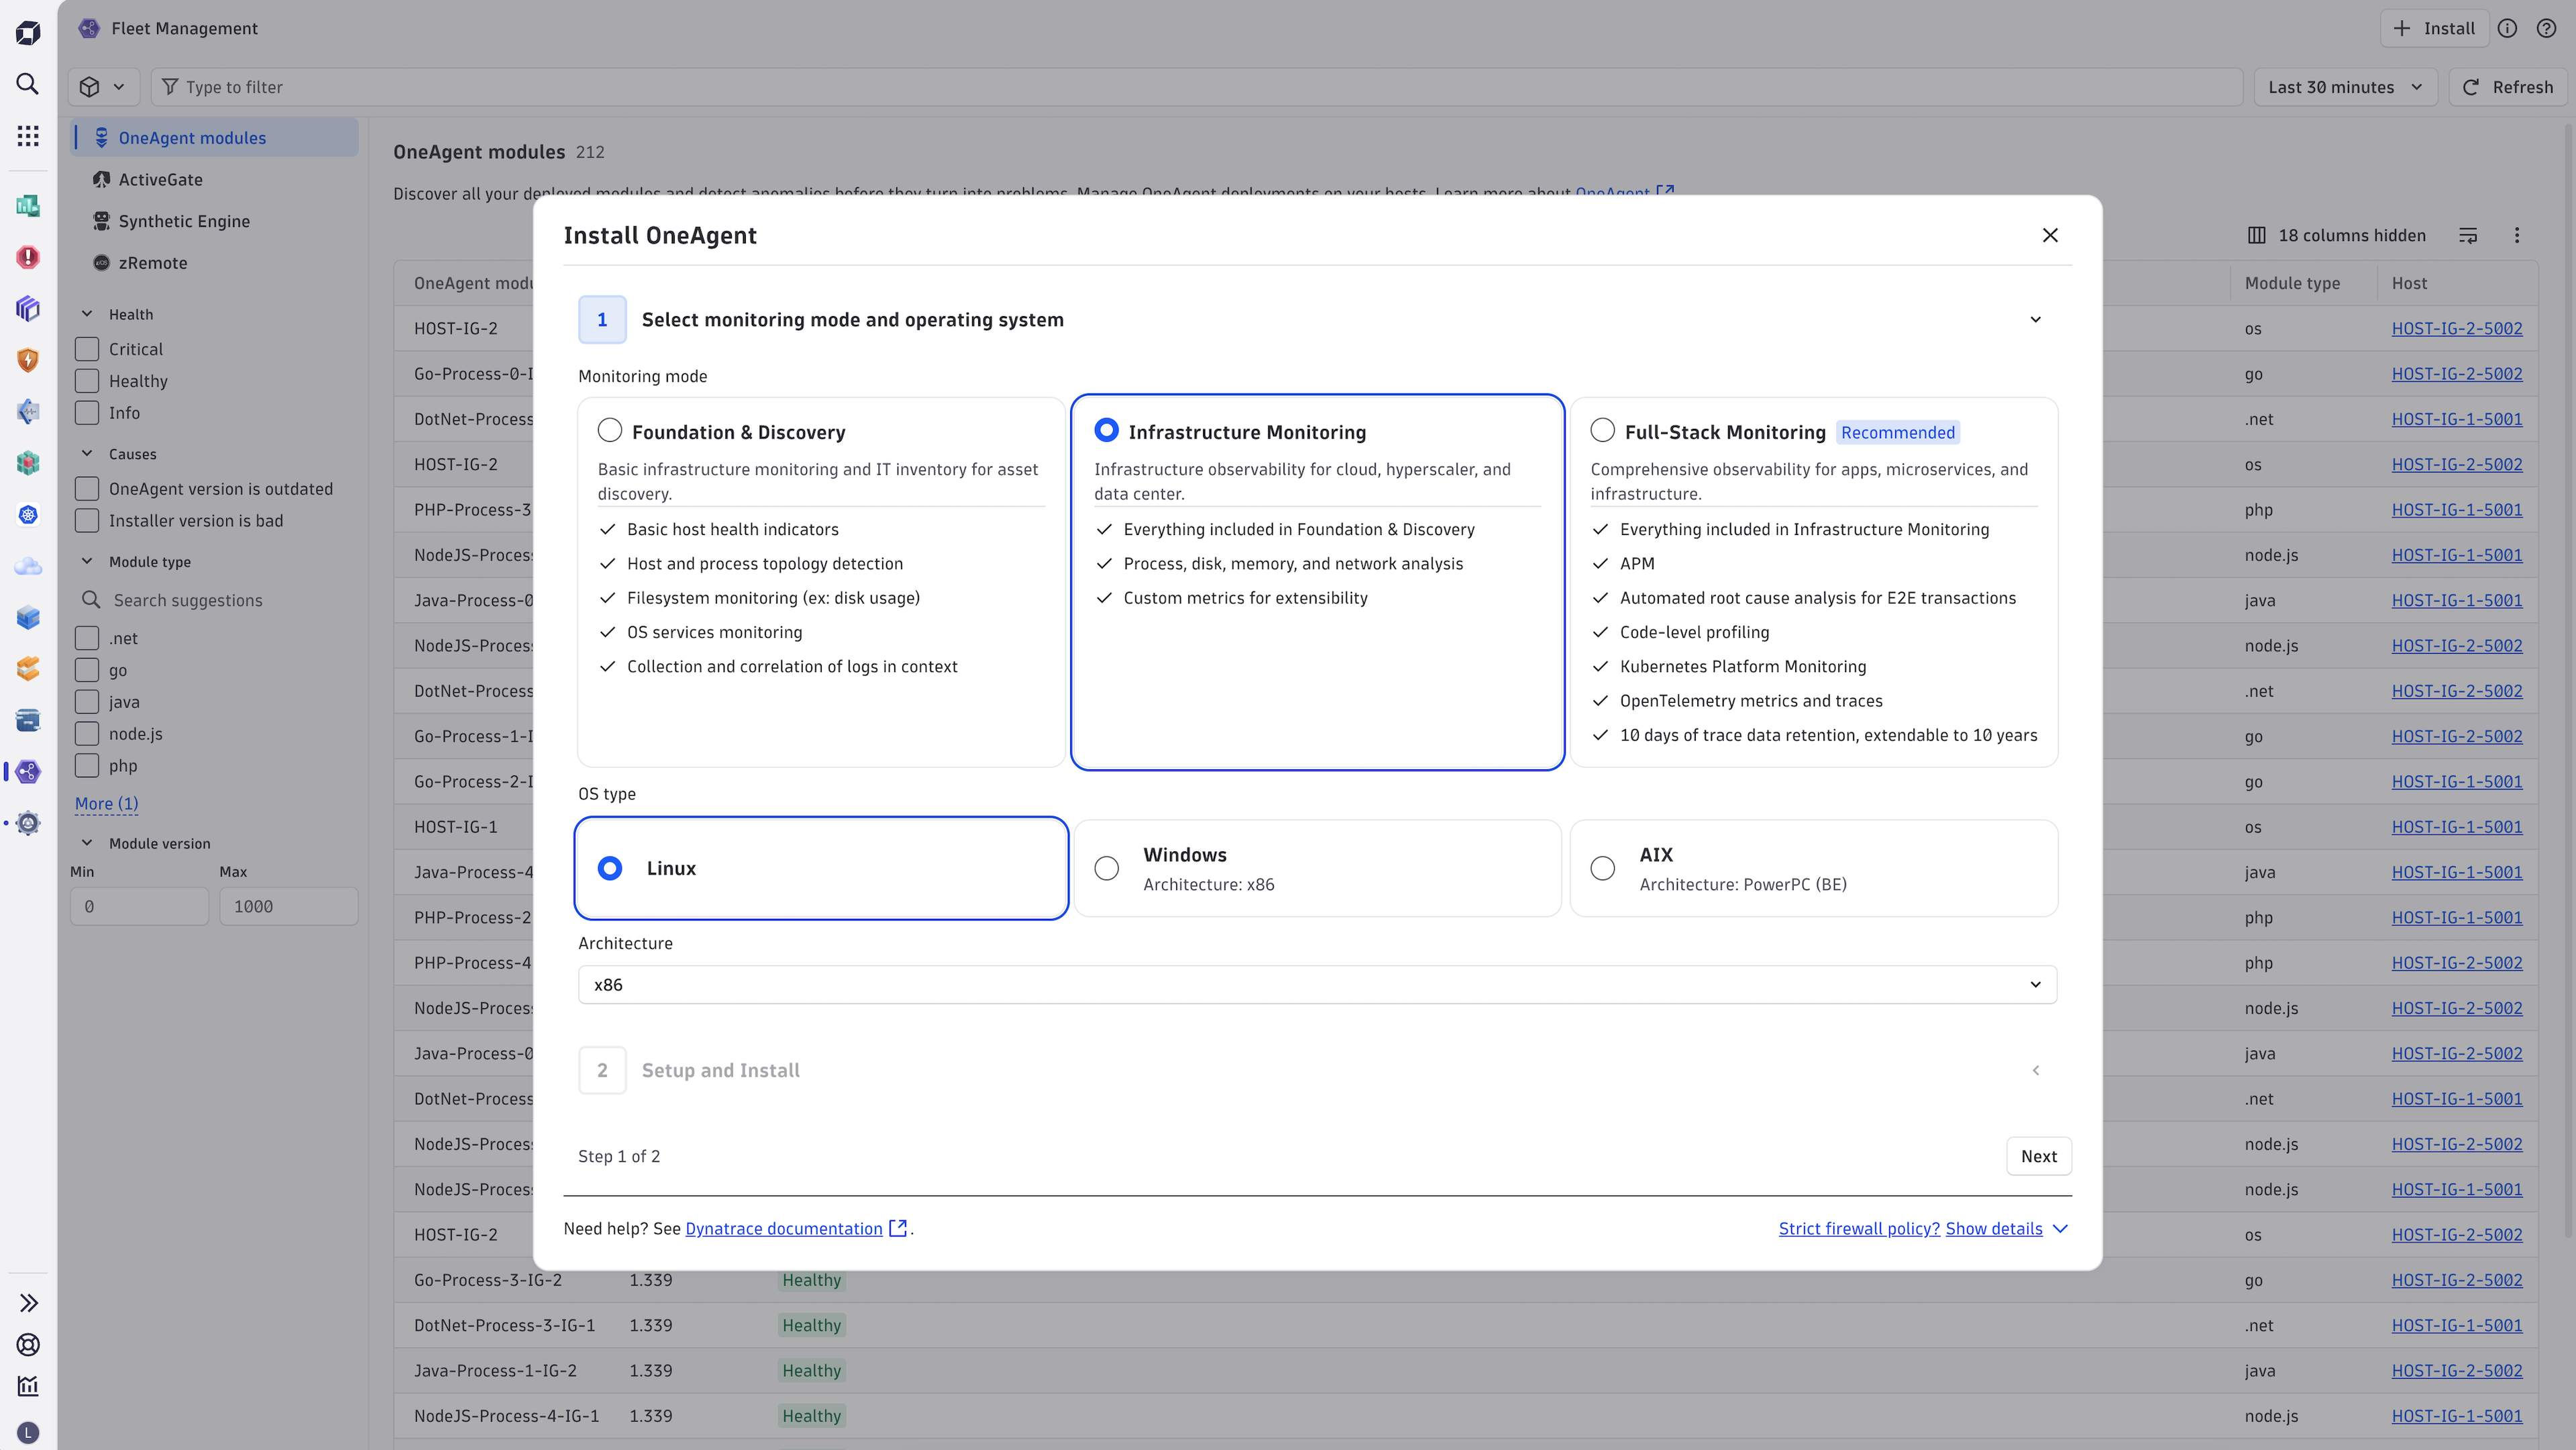
Onboarding improvements. Faster time to value when installing new OneAgents and ActiveGates, directly from the app.
Quick monitoring configuration overview. See the configurations applied to each component, including those inherited from the environment or group level.
Granular permission management. Flexible control over who is authorized to perform specific actions
Navigation Fleet Management provides an overview of all fleet components deployed in your environment. You can switch between component types and drill down into individual entities. The following components are currently available:
To install new components, select Install OneAgent or Install ActiveGate in the upper-right corner.
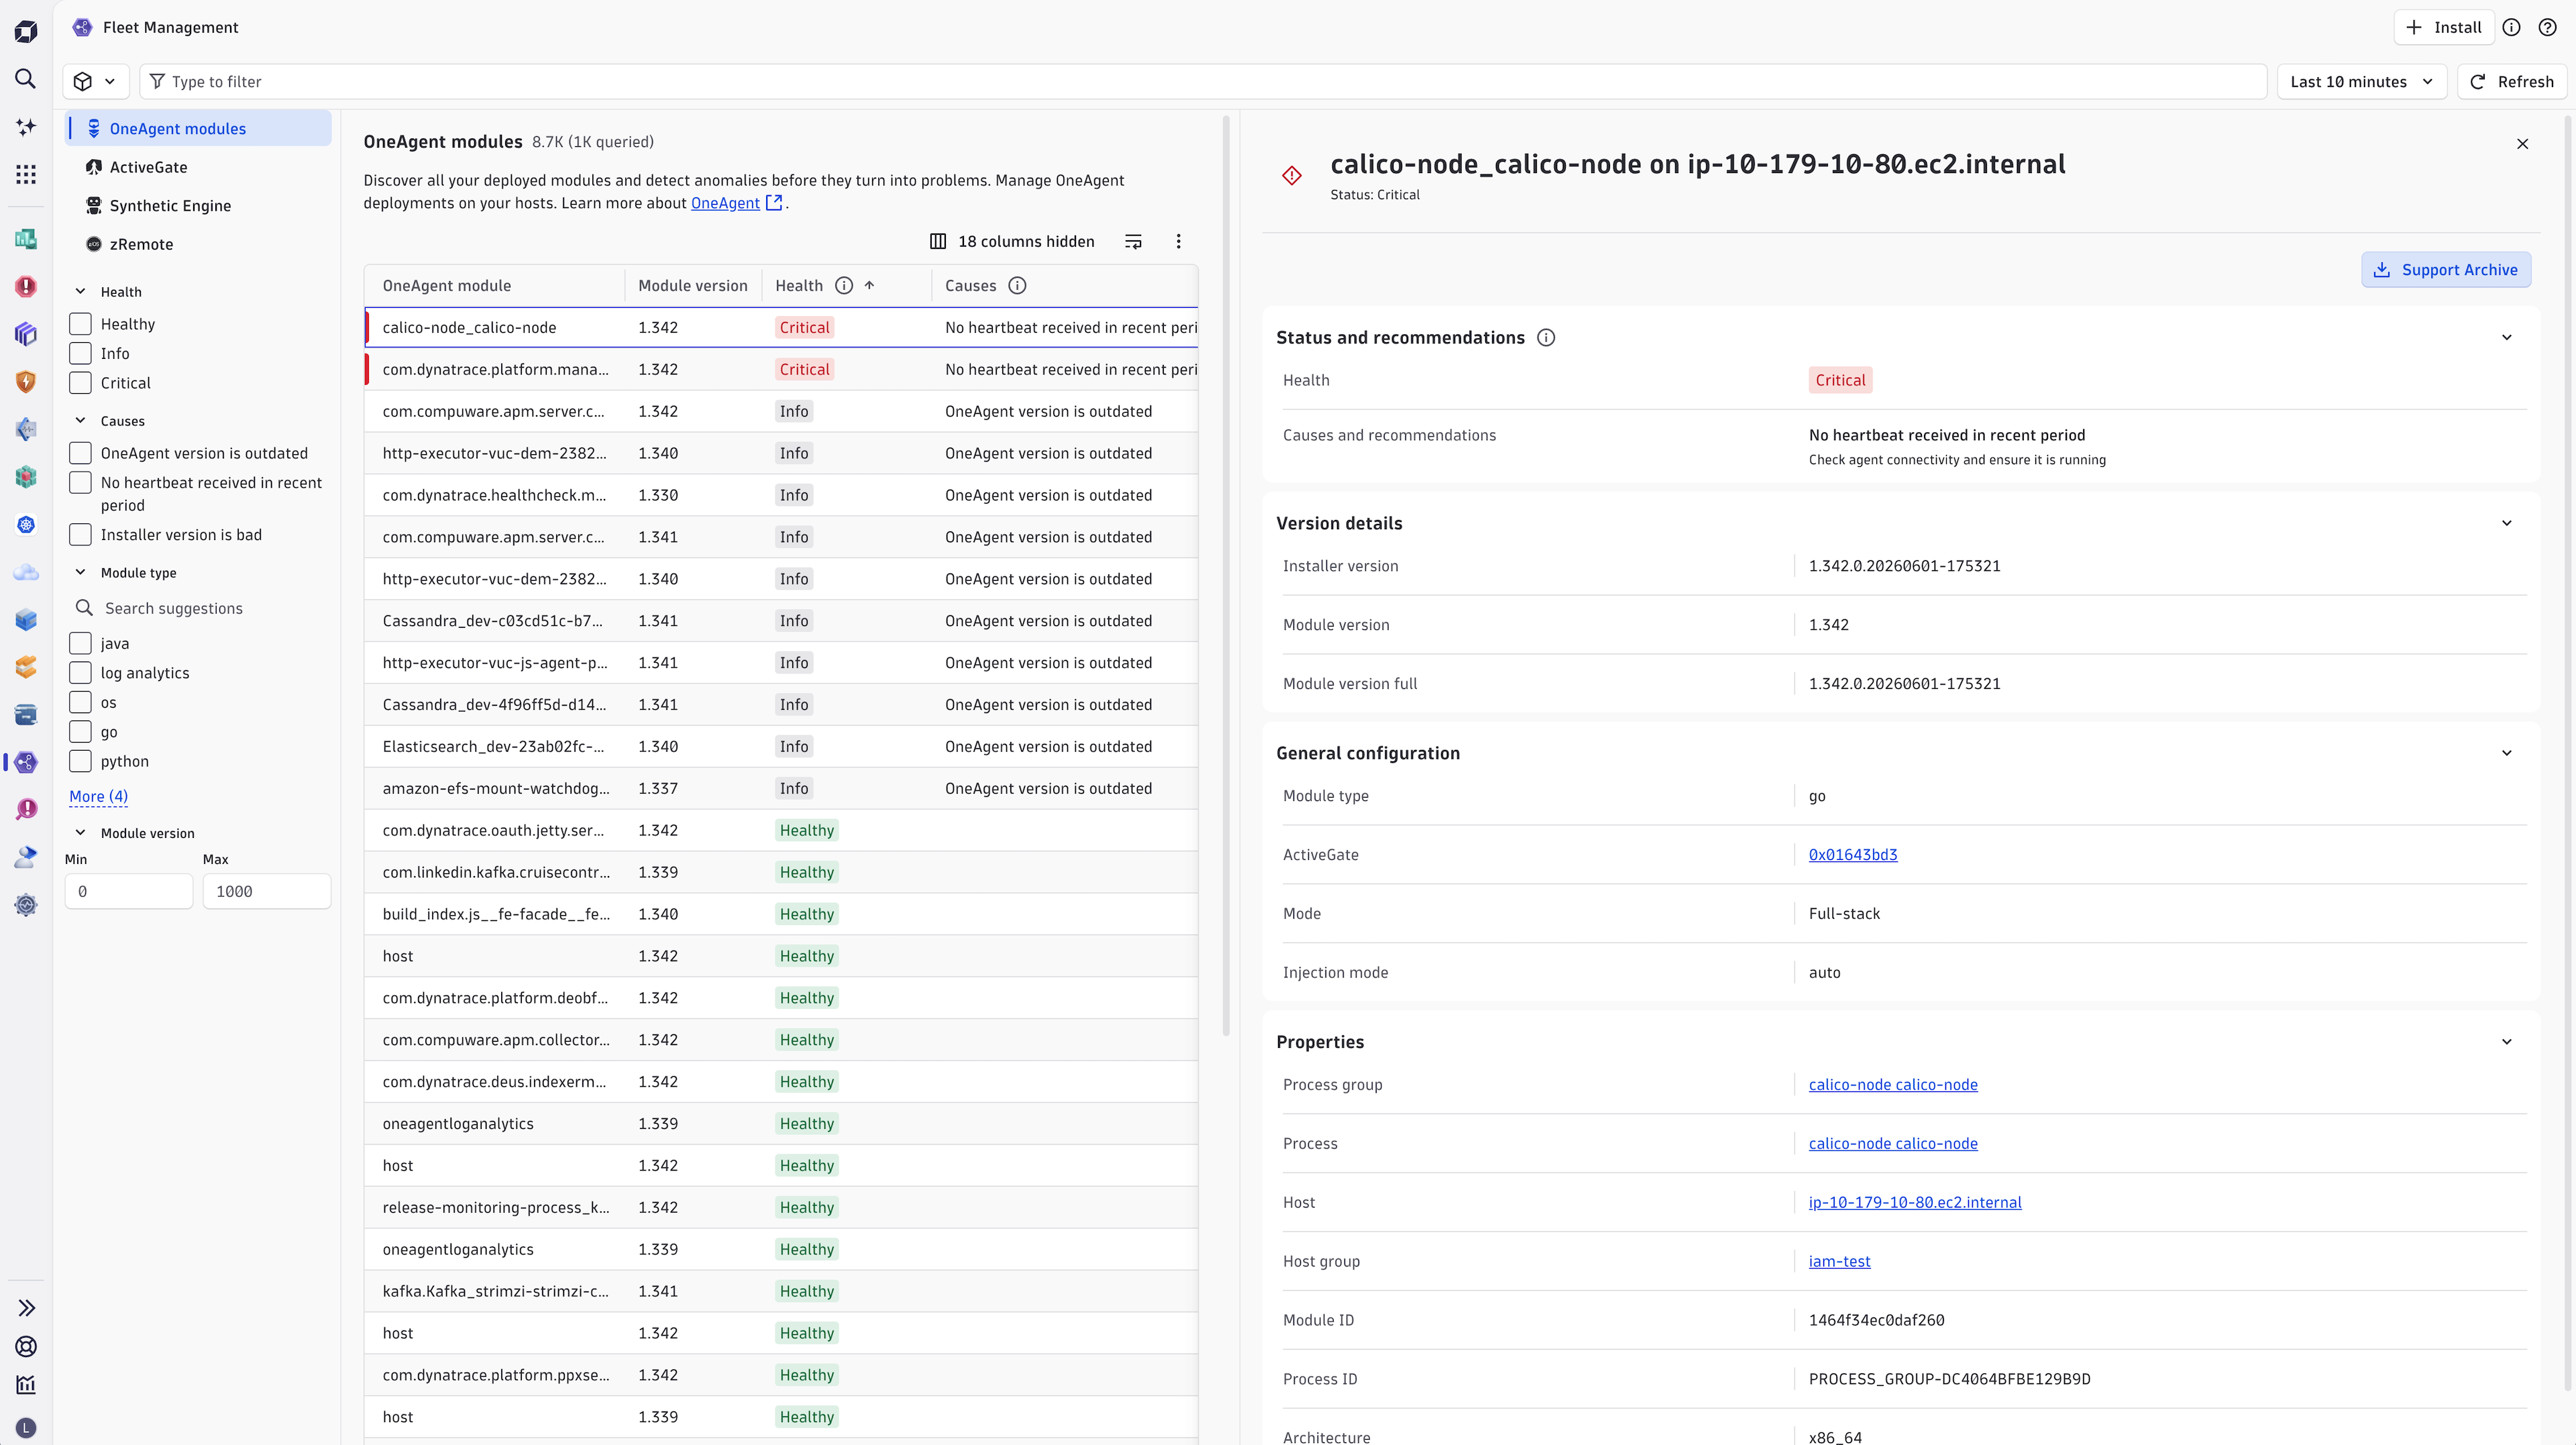
View entity details Selecting an entity opens a details panel that groups attributes into sections such as Status and recommendations, Version details, Properties, and Modules enabled. The exact sections depend on the entity type—for example, ActiveGates that handle synthetic traffic include a dedicated Synthetic monitoring section. The top of the panel shows the entity name, current status, and purpose, together with quick links:
Explore data in Notebooks and Dashboards All Fleet Management data is stored in Grail and is DQL-queryable. From any entity list, you can:
View health and recommendations Fleet management app groups your fleet by component type and health condition, so you can quickly see which components need attention. The view is scoped to what's present in your environment, and items with the highest impact appear first. Select any entity to open its details panel. The Status and recommendations section shows the current health state.
Manage updates The Version details section shows the current version, the configured target version, auto-update status, the update window (if defined), and the next scheduled update. Configure updates flexibly via the update setting by:
Download support archives To get started with troubleshooting a selected OneAgent or ActiveGate, you can download support archives for a selected time period. You can analyze it yourself or share the archive with Dynatrace Support for further assistance.
Manage network zones Fleet Management provides an entry point to the network zones configuration. You can also find your defined Network zones in Settings under Fleet Management > Network zones, and manage them (if you have the required permissions).
Fleet management app also supports the new Cloud Platform Monitoring for AWS, Azure and Google (GCP). To get started, review and follow the setup documentation for AWS, Azure and GCP.
In Autodiscovery, the ingest rules count is now a link that shows the rules evaluated for that log source.
Always show the status column with the enable/disable toggle in rule-like settings tables.
Fixed an error when expanding a rule row in the rules evaluated on a log source dialog.
Renamed "entity" to "scope" in the autodiscovery log sources UI (scope details sheet, scope summary, row action menu and related messages).
Added an "Operation mode" option to Feature Flags that lets you configure the log ingest delay.
Fixed the CPU usage limit field to show validation errors while typing instead of only after unfocusing, and to replace the hint with the error consistently.
Removed the option to switch back from unified enrichment settings for tenants in phase 3 and above.
Fixed custom log source rules not highlighting invalid path or attribute fields when submitting a form with untouched required fields.
Warn when a custom log source path doesn't look like a valid Unix or Windows path.
Sources matched by ingest rules are now visible in the rules table.
Hide attributes in custom log source details for Windows Event Log sources.
Reverted preserving last opened tab in log module settings widget.
The auto-discovery sheet heading now shows the selected entity's name and type, and entity scope types in the log rule dialogs are shown as a "Type: …" chip instead of an icon.
Added an "Ingest rules" column to the auto-discovery log sources list showing how many ingest rules apply to each log source.
Replaced log ingestion coverage column with log file status column in auto-discovery log sources list.
Removed the coverage percentage from entity tiles and the average coverage column from entity lists in auto-discovery.
Log source summary now shows a warning instead of an error when you lack permission to read system logs.
Auto-populate enrichment value based on path and attribute key, and warn when the value references a wildcard that doesn't exist in the path.
Users with restricted IAM policies on the autodiscovery section were incorrectly blocked from accessing it. The app now sends the right context when checking permissions, so the server can give a clear yes or no instead of an inconclusive answer.
Tab navigation now uses URL paths (/sources, /ingest-rules, etc.) instead of query params, so deep links, back button, and browser history work per tab.
Matcher values are now displayed as compact chips for improved readability.
Matcher rule chip values now display their full text without truncation.
Autodiscovery: preserve expanded rows, search, filters and sorting when switching entity types.
Sorting the inner table no longer collapses the outer one, and the table no longer stretches to fill the whole screen when few rows are shown.
Added a regex tester to the sensitive data masking rule modal, using server-side evaluation to validate the expression and preview the masked result against sample logs. Gated behind the log-module-settings.regex-tester feature flag.
Added a link to regex examples in the sensitive data masking rule modal.
Added a "Sources configuration" sub-tab that lets users define rules controlling encoding, binary content, and log rotation per log source.
Added JSON rules management under the Processing rules tab.
Grouped processing rules settings under a single tab.
Added a binary detection algorithm select to advanced log settings.
Renamed the Event Suppression tab to SFM Events and updated the UI text to explicitly mention Self Monitoring Events (SFM).
Updated the SFM suppression tab description and added a documentation link anchor.
Single-object settings views (Discovery and processing, Opt-in feature flags, Resource allocation) now show a banner when child entities override the current scope's settings.
"Show entities" on the overriding settings banner now opens the platform's Custom settings panel instead of a separate entities list.
Hid the custom settings button in the widget's title bar, keeping the per-tab overriding entities banner as the single source of truth.
CPU usage limit field is now bounded between 0.01 and 100 and accepts decimal values; the hint shows the range and uses a "Learn more" link.
Replaced the documentation links in the advanced settings descriptions with a trailing "Learn more" link.
Added a documentation link to the CPU usage limit field description and to the opt-in feature flags section.
Moved the "Other OneAgent features" link into the advanced log settings section.
Improved the sub-tabs layout in the settings widget.
Updated the widget heading and feature flags tab title.
Added more meaningful placeholders.
Added a separate icon for system logs.
Allowed per-entity smartscape IDs (dt.smartscape.k8s_pod, dt.smartscape.k8s_namespace, dt.smartscape.k8s.entity, dt.smartscape.k8s_cluster) as show_log_sources intent params.
The show_log_sources intent now accepts classic namespace and pod id; added the alias dt.entity_source.id for the classic entity id, mirroring dt.smartscape_source.id.
Auto-expand the Advanced section for a custom log source path when it already has enrichment data.
Aligned the multiline search expression in masking rule details so wrapped text stays next to its label.
Fixed different log level values of an Ingest rule matcher all showing up as ALERT when editing.
Fixed a crash when opening autodiscovered log sources from an intent.
Fixed a crash in the custom log source settings widget when useWatch returns undefined on the first render.
Fixed quickly edited fields in log rules or resource allocation settings not triggering the unsaved-changes prompt.
dt.sfm.da.aws.log.records.count metric.view-entity-list intent, allowing other Dynatrace apps to open the Explorer pre-filtered to a specific OneAgent's modules. Added an oneAgent column and filter to the modules InvEx config.storage:system:read permission can now access the AWS, Azure, and GCP connection widgets.Share Feedback link to the help menu.storage:system:read permission can now access the AWS, Azure, and GCP connection widgets.Share Feedback link to the help menu.storage:system:read permission can now access the AWS, Azure, and GCP connection widgets.Share Feedback link to the help menu.storage:system:read permission can now access the AWS, Azure, and GCP connection widgets.Share Feedback link to the help menu.Share Feedback link to the help menu.Manage updates and Network zones buttons in the Fleet Management header being hidden for users without install permissions. Only the Install action is now permission-gated. (ICP-8258)metrics field.Properties section of the details sheet opening in the same tab instead of a new tab.metrics field.Properties section of the details sheet opening in the same tab instead of a new tab.k8s.cluster.uid instead of the cluster entity ID, ensuring accurate results when viewing log sources scoped to a specific cluster.k8s.cluster.uid instead of the cluster entity ID, ensuring accurate results when viewing log sources scoped to a specific cluster.8bd0ba4: Update timestamp and splitting rules JSON detection to show "No" when detection is explicitly disabled and an empty-state placeholder when it is unset.
ee4fce6: Fixed auto-discovery DQL queries being cancelled when switching browser tabs
25774b3: Fixed success and error toasts when deleting objects from log module settings tables
643fbc5: Timestamp and Splitting rules > treat null value for formatDetection as "true" for backwards compatibility
91c186d: Show a neutral banner in the autodiscovery status section when status information is not available
4208d32: Show appropriate message when user does not have configuration read permissions.
####Patch Changes
table.
be found in Azure