OpenTelemetry Collector distributions compared: Core, Contrib, OCB, and vendor builds. Which one should you use?
Compare OpenTelemetry Collector distributions: Core, Contrib, OCB, and vendor builds to choose the right fit.
Tutorials, tips and resources for engineers on cloud technologies and observability

Compare OpenTelemetry Collector distributions: Core, Contrib, OCB, and vendor builds to choose the right fit.
How Dynatrace and an AI coding assistant can bridge the gap between "something is slow" and "here is the fix.”
Learn why Kubernetes pod-level resource discrepancies happen, when they apply, and how Dynatrace surfaces the correct value.
PHP2Shell: Two critical PHP flaws under active attack. Update now and use Dynatrace to find affected PHP processes.
Deploy automated honeytokens in Kubernetes with Koney
Explore how Dynatrace integrates seamlessly into your DevSecOps processes providing application-level insights to security findings across the SDLC.
React2Shell CVE-2025-55182 exposes servers to remote code execution. Learn risks, impacted frameworks, and urgent remediation steps.
Boost supply chain security with Dynatrace using real-time detection and automated workflows against malicious packages.
Learn how attackers exploit Kubernetes container misconfigurations and how to defend against them with practical examples.
Here's how to use the newly published Snyk integration to create actionable Jira tickets.
Auth0 monitoring with Dynatrace enables organizations to gain unprecedented insights into authentication, security, and identity events.
This blog covers three building blocks of handling threats: Leave no gaps, get the right eyes on it, and respond quickly.

Using Spring4Shell as an example, discover how Dynatrace can detect and prevent exploitation on multiple layers.
Cyberattacks are increasingly shifting user identities. Discover show sign-in monitoring is crucial to secure user identity.
By combining different data sources like logs and runtime context, Dynatrace can help improve detection accuracy and create actionable findings.
A Kubernetes misconfiguration can lead to security vulnerabilities. Learn how attackers exploit them, and how to mitigate attacks.
All too often, Kubernetes misconfigurations become security misconfigurations. Learn why, and how to avoid them.
Quickly find and mitigate the IngressNightmare vulnerabilities affecting Kubernetes clusters with Dynatrace.
VMSA-2025-0004 contains three vulnerabilities in VMware ESXi. Quickly find affected systems and automate remediation using Dynatrace.
Apache Struts CVE-2024-53677 introduces risk to the file upload mechanism. We identified early indicators to mitigate its impact.
Broken Apache Struts 2: Technical Deep Dive into CVE-2024-53677
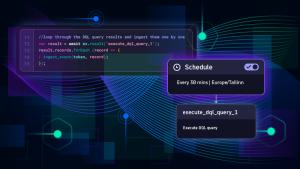
Detect threats like DNS tunneling with custom Dynatrace security events.
The Dynatrace observability and security platform quickly allows you to understand what is running within your environment.
The Qualys Threat Research Unit (TRU) discovered a Remote Unauthenticated Code Execution (RCE) vulnerability.
This blog post demonstrates how to use Dynatrace Automations to build a runbook that combats sophisticated security incidents using honeytokens.
Uncover advanced threat detection strategies using Dynatrace Security Analytics and Falco Alerts, proactively safeguarding your environment.
Detect and investigate malicious activity using Dynatrace Grail, enhancing security posture across multicloud environments.
Details on a critical vulnerability (CVE-2022-42889) and its impact, emphasizing the need for timely patching and security measures.
Gain insights into mitigating Spring4Shell vulnerabilities in the Java Spring Framework, safeguarding applications from potential threats.