Runtime Vulnerability Analytics
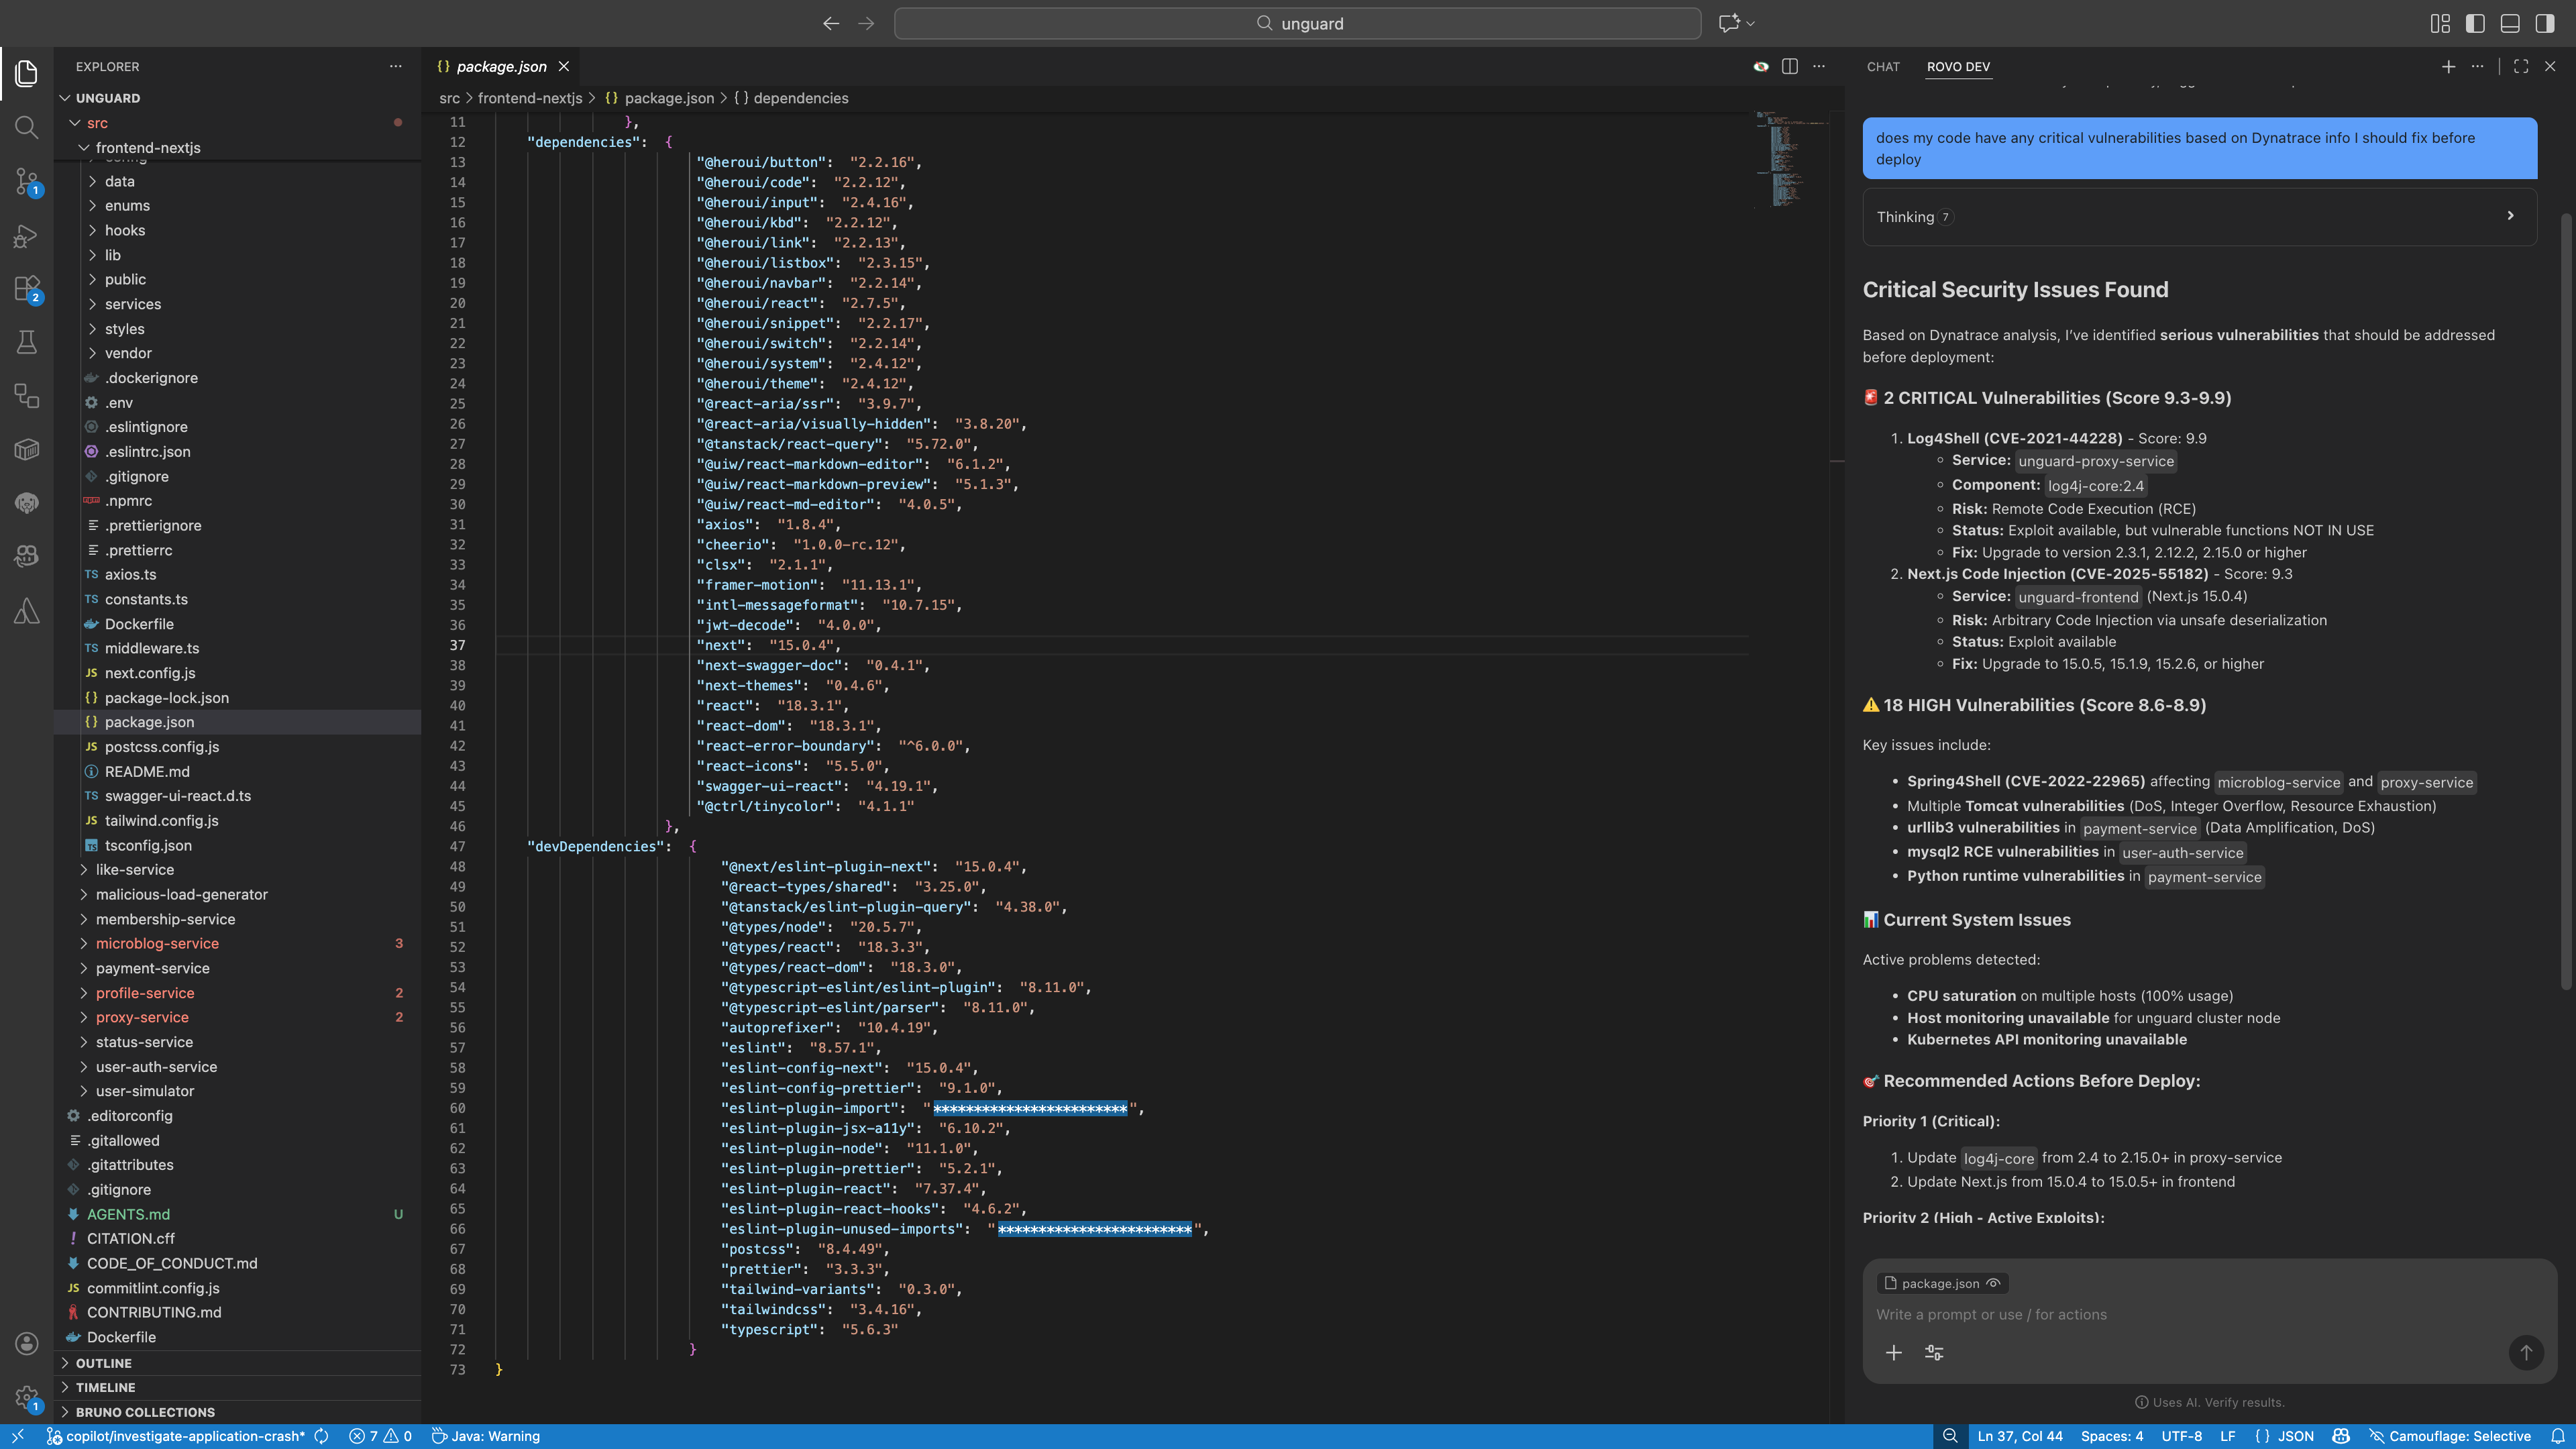
Dynatrace uses real-time runtime context to continuously detect and prioritize vulnerabilities, so your team acts on signal, not noise.
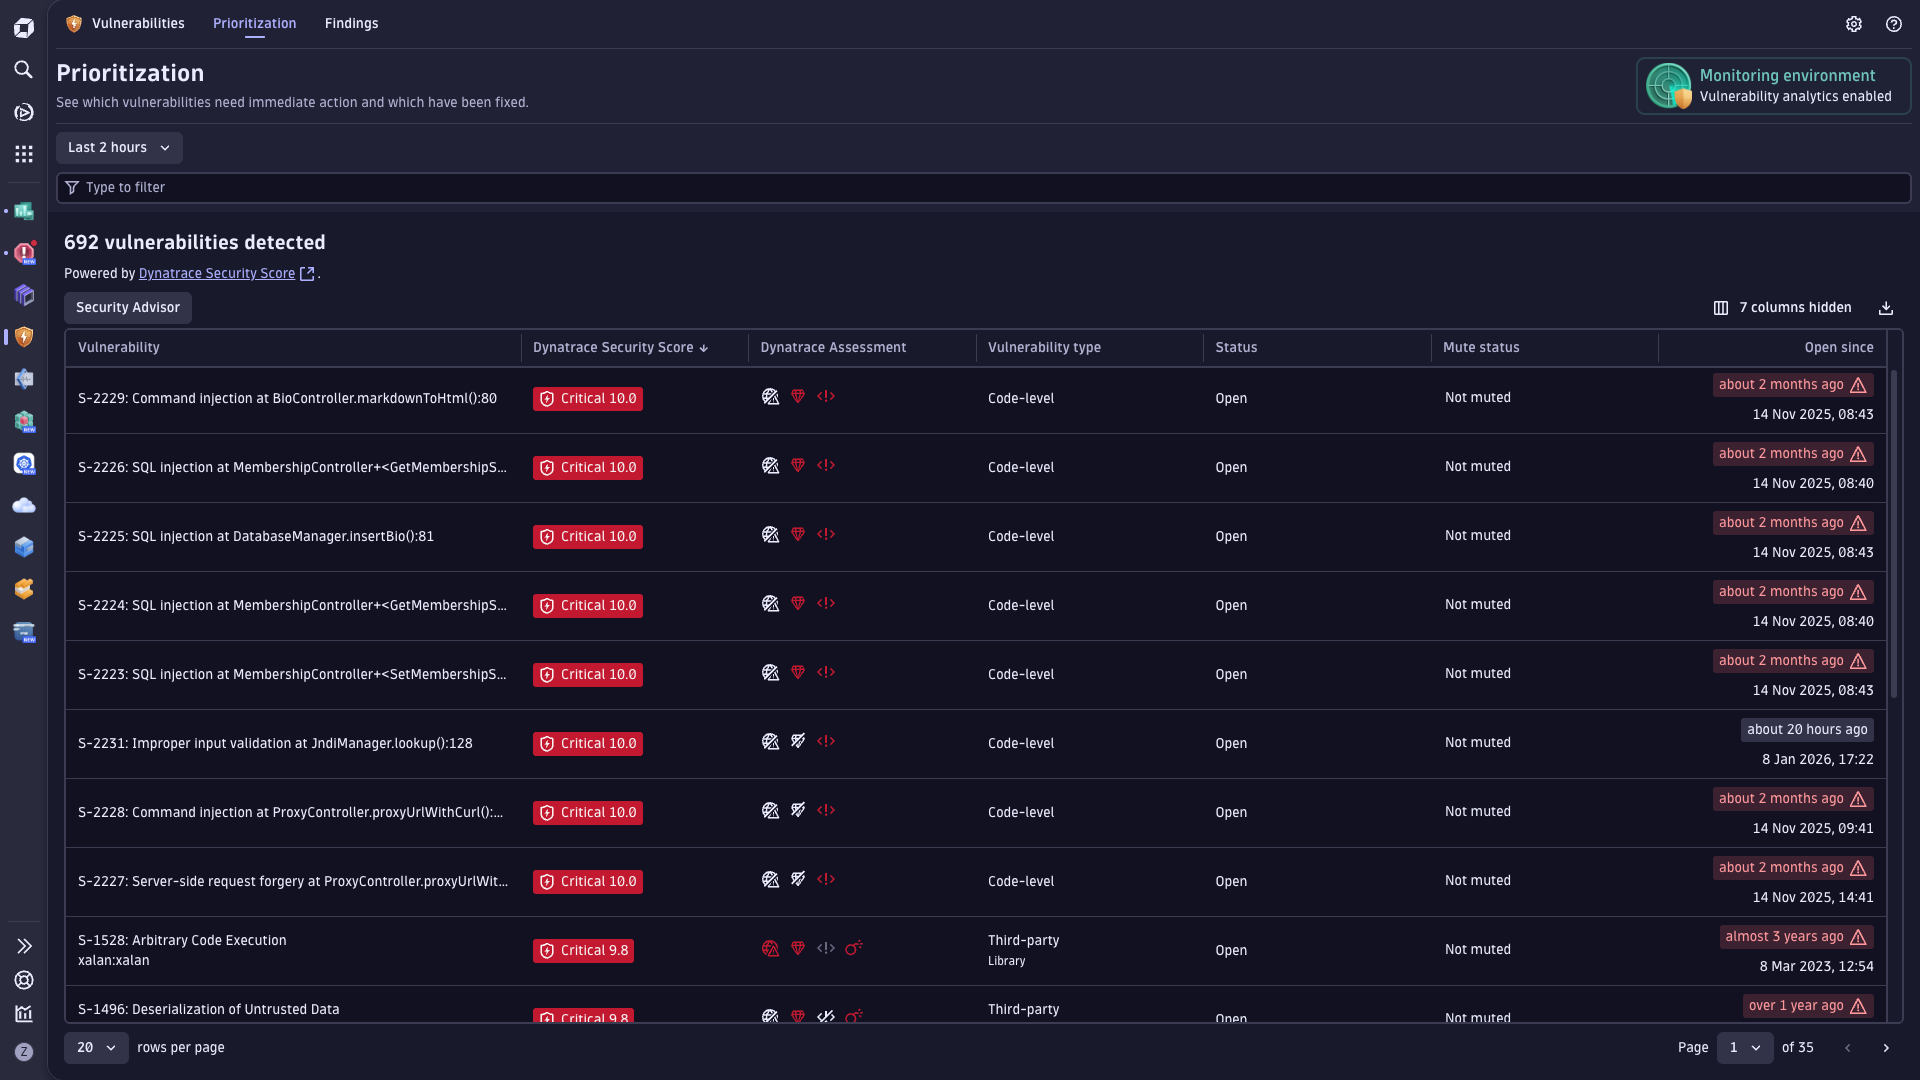

The context you need to cut through noise
Most scanners dump thousands of findings with no production context. Dynatrace analyzes runtime behavior to surface only what's active, reachable, and impacting live services.
Protect production reliability with real runtime risk
A vulnerability that isn't reachable in production isn't worth your team's time. Dynatrace continuously monitors runtime behavior, correlates vulnerabilities with live service context, and surfaces only the findings that pose actual risk so teams act on signal, not noise.
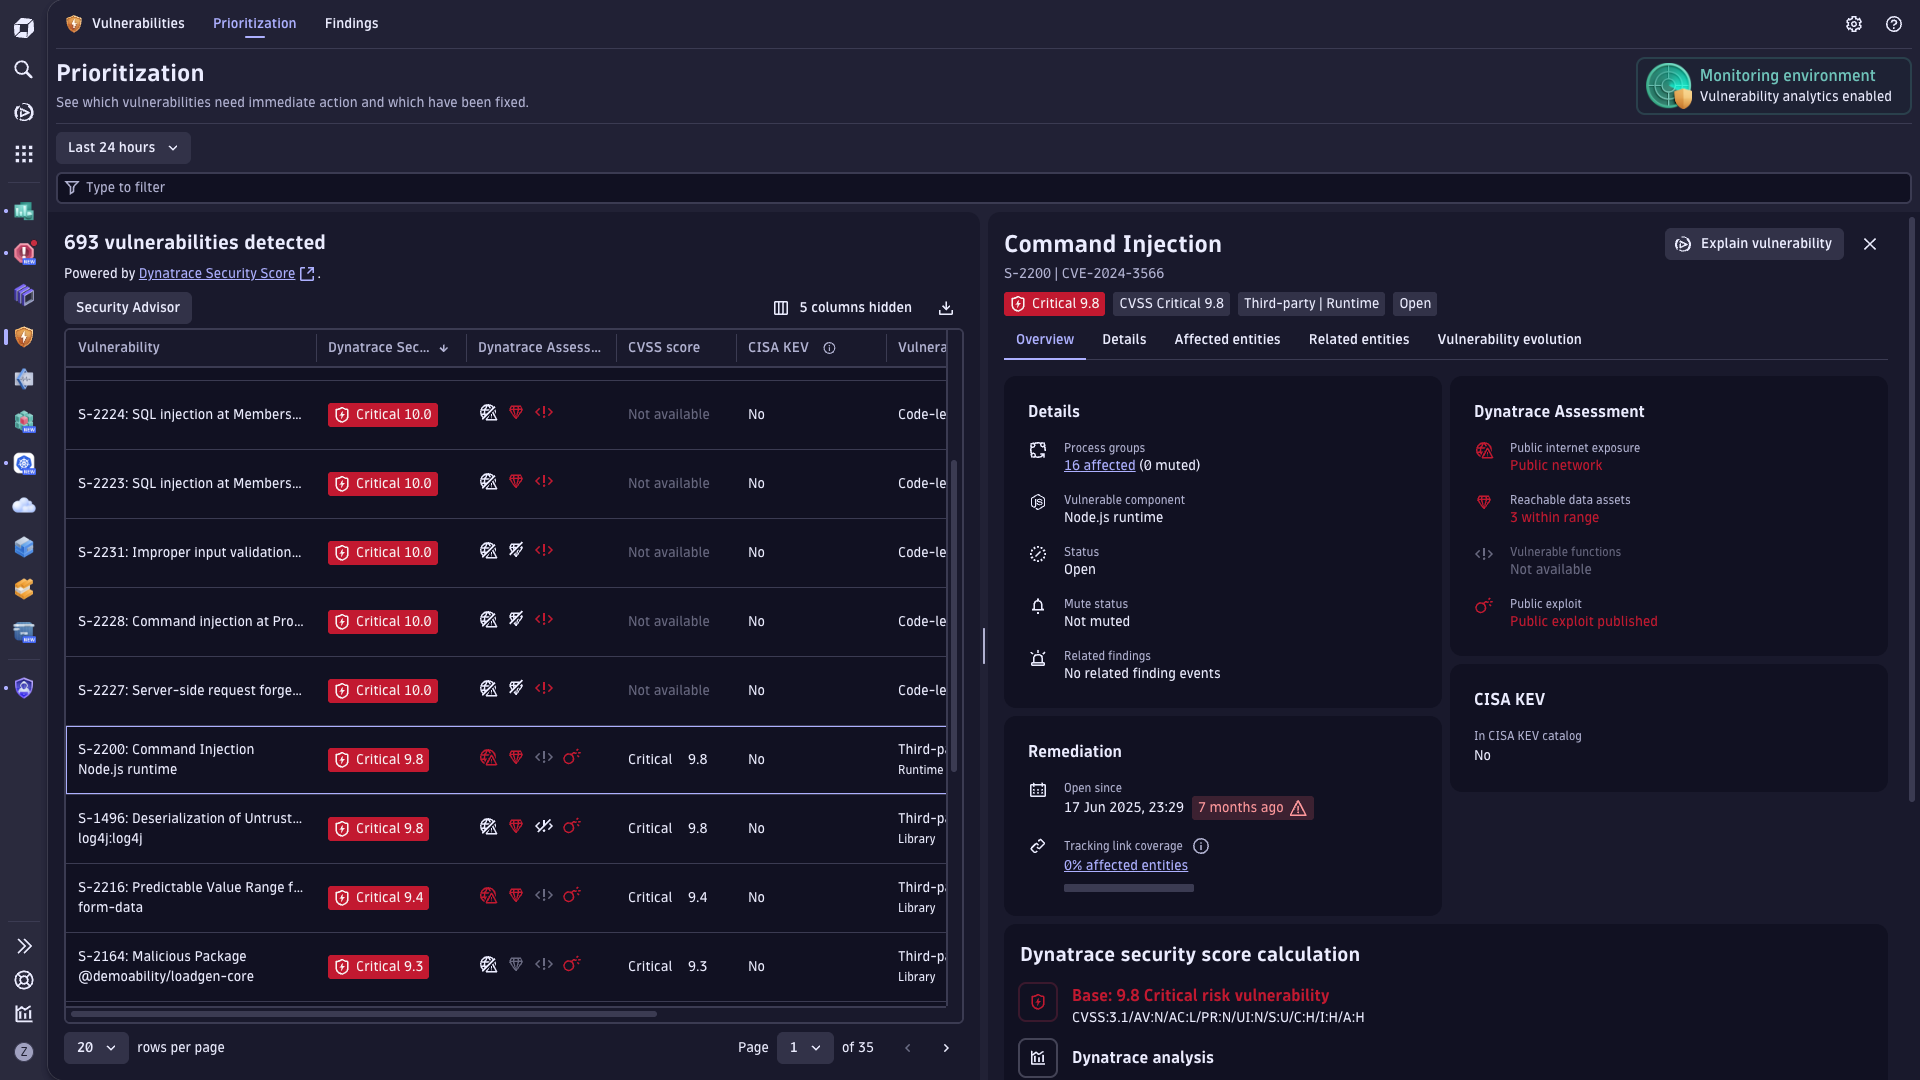
Maximize uptime for Kubernetes workloads
Kubernetes environments move fast and expose new attack surface constantly. Dynatrace detects configuration risks, third-party dependency exposures, and active threats across your workloads, then triggers automated remediation workflows to reduce MTTR before users feel the impact.
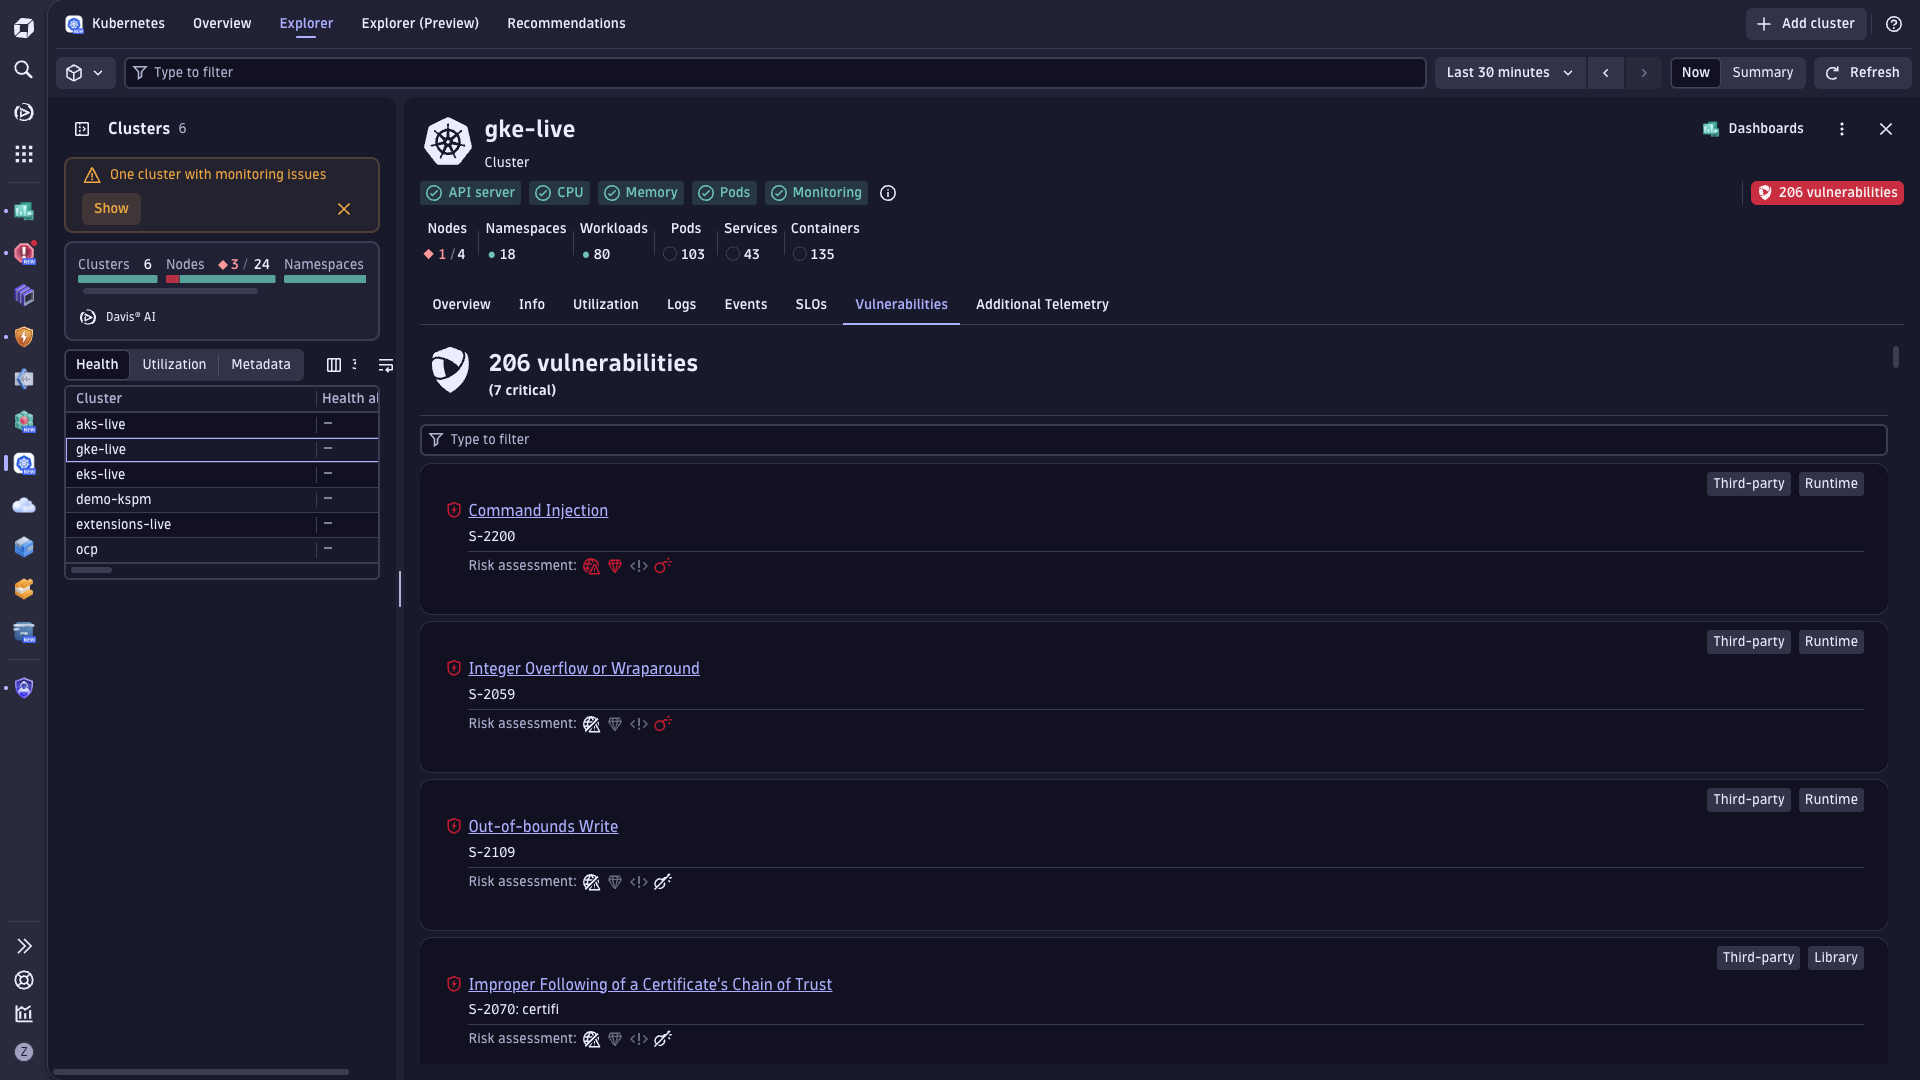
Automate the path from finding to fix
Triaging and remediating vulnerabilities manually doesn't scale. Dynatrace automatically prioritizes findings using runtime risk and environmental context, guides developers with precise fix recommendations, and uses agentic workflows to accelerate resolution and validate the fix.