
CrowdStrike
Outage, incident, or breach? Dynatrace and CrowdStrike connect logs, security, and application context so teams can investigate with a shared view.

Shared context. Smarter answers. Lower costs.
Connect logs, security, and application context to streamline investigations and reduce duplicate data and cost.
How Dynatrace and CrowdStrike work together
Native integrations connect logs, security, and observability context to accelerate investigations and help reduce duplicate data and cost.
Bring CrowdStrike context into Dynatrace
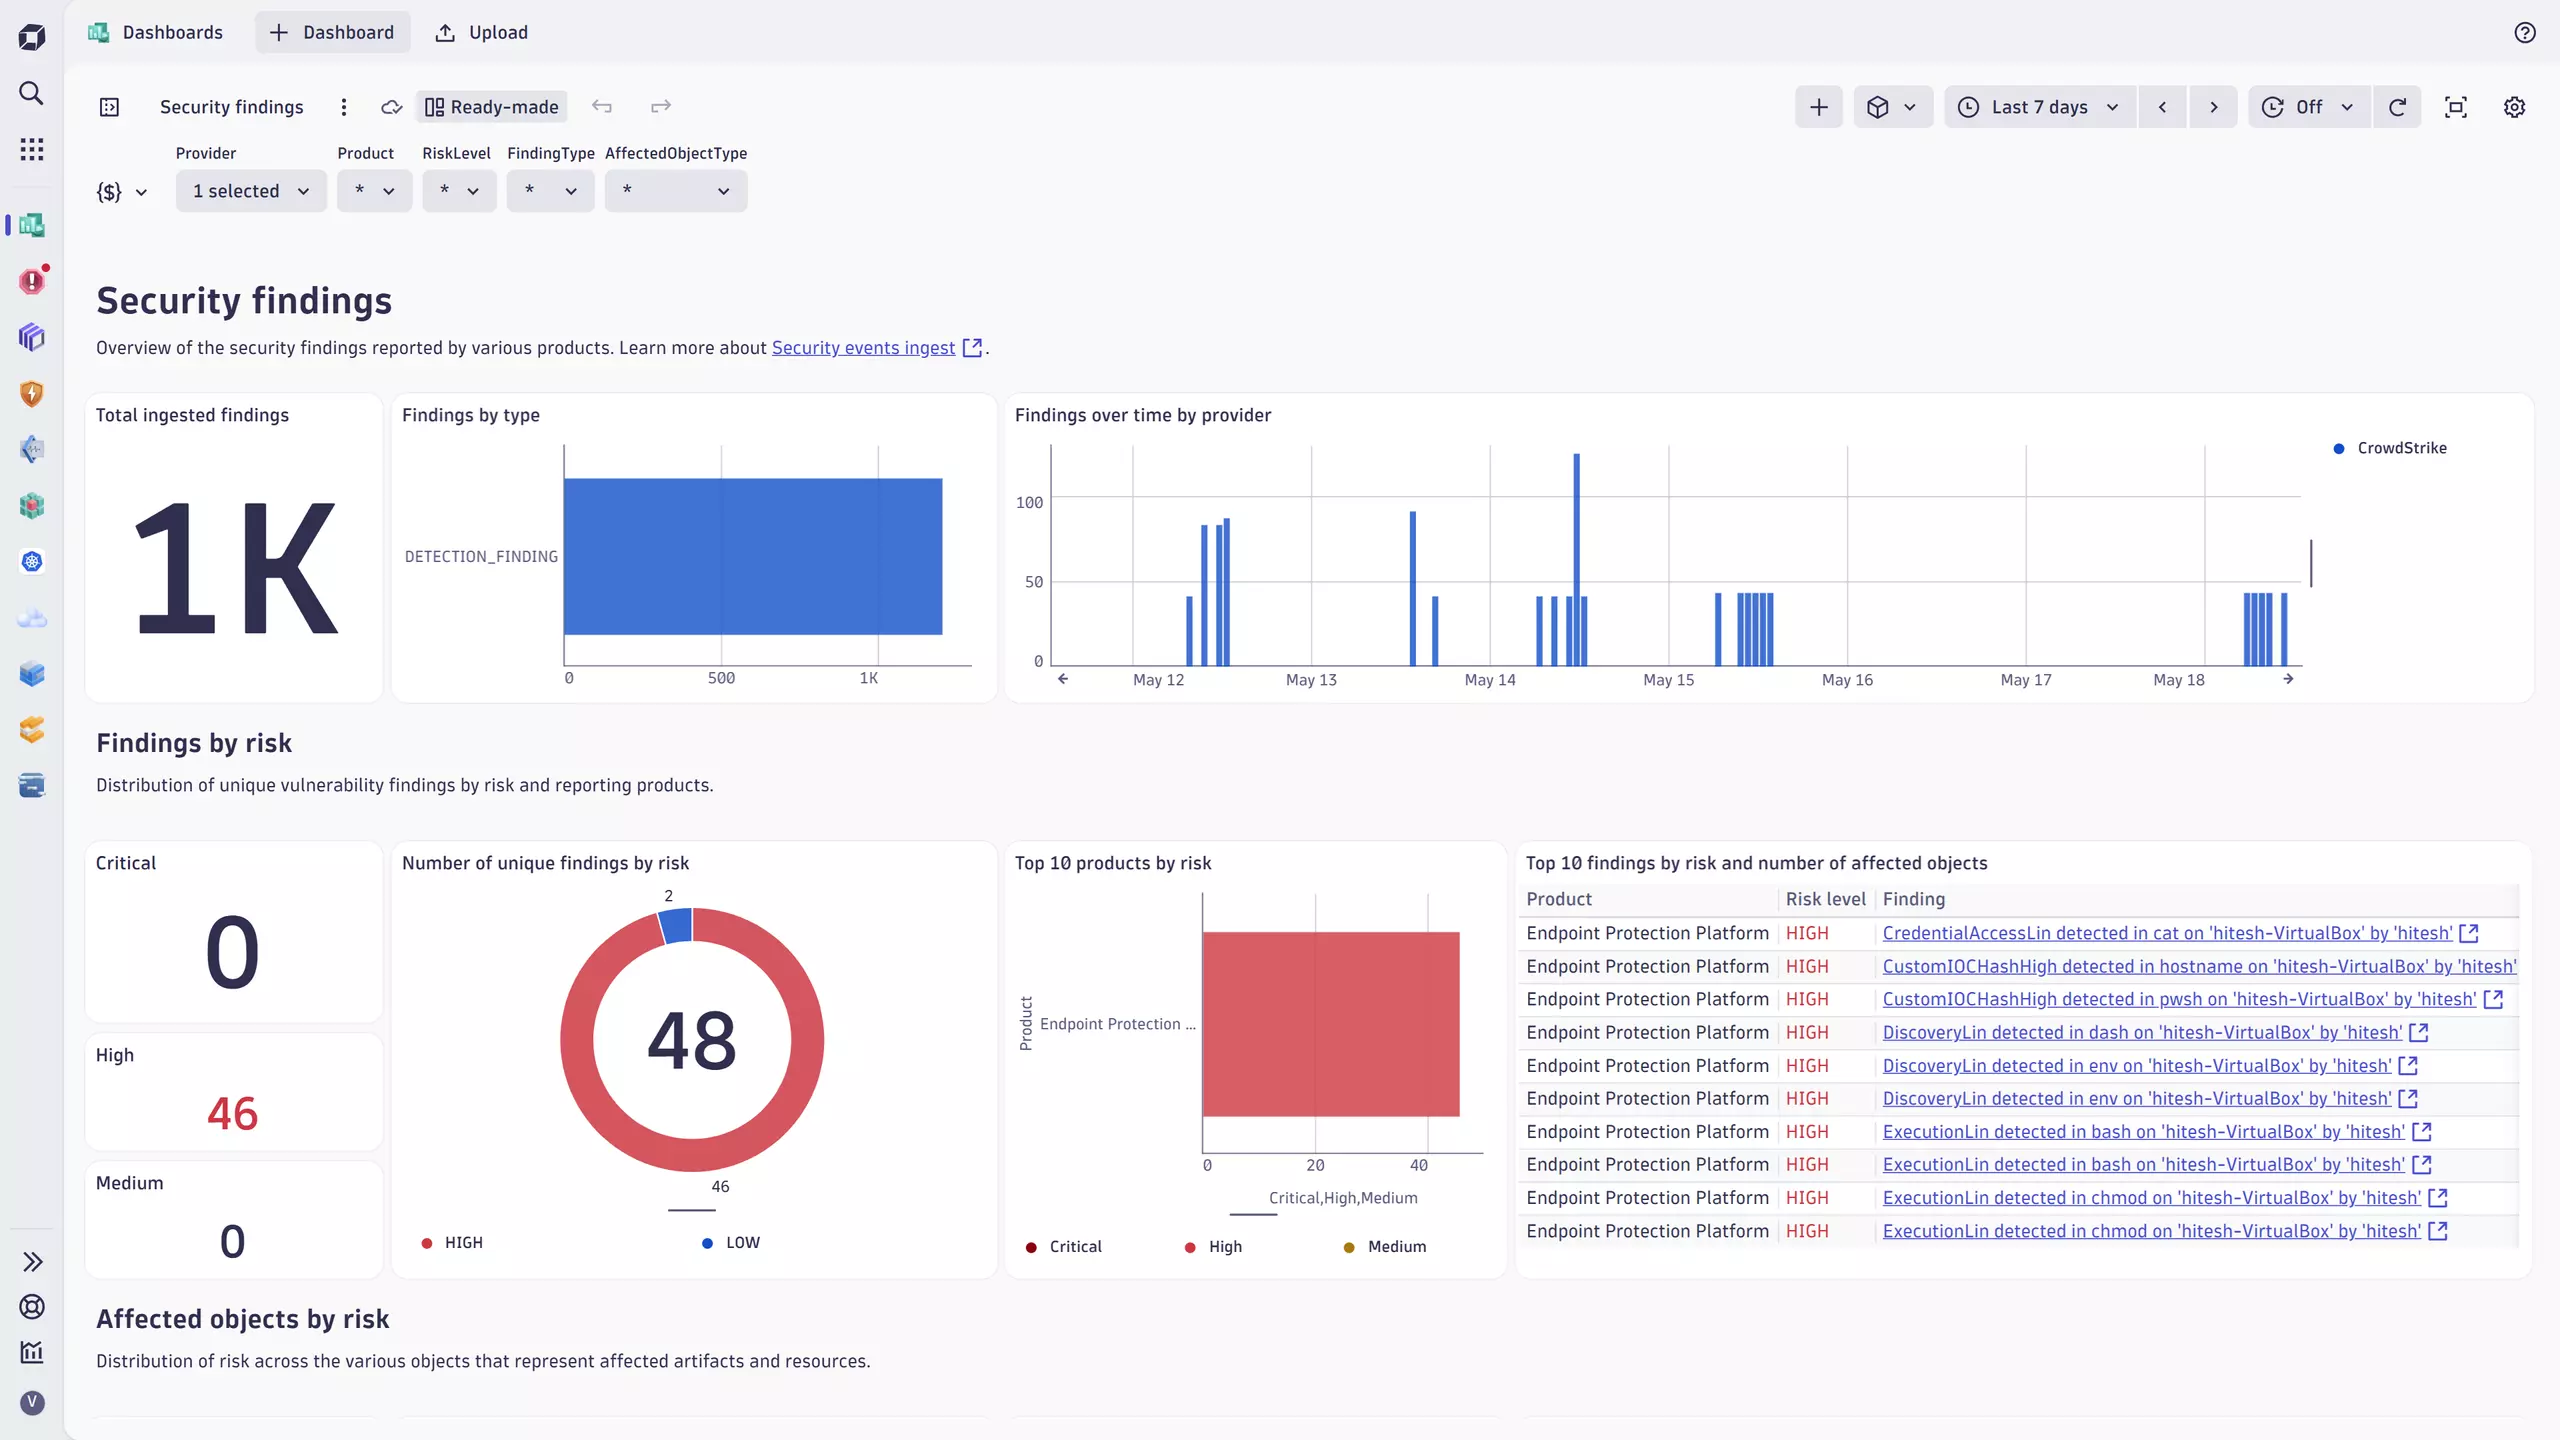
- Security findings: Bring CrowdStrike detection findings into Dynatrace for investigation.
- Application context: Correlate security findings with logs, application, and infrastructure context.
- Impact analysis: Use logs and application topology to understand which services may be affected.
- Shared workflow: Investigate security and application context together in Dynatrace.
Bring Dynatrace context into CrowdStrike Falcon
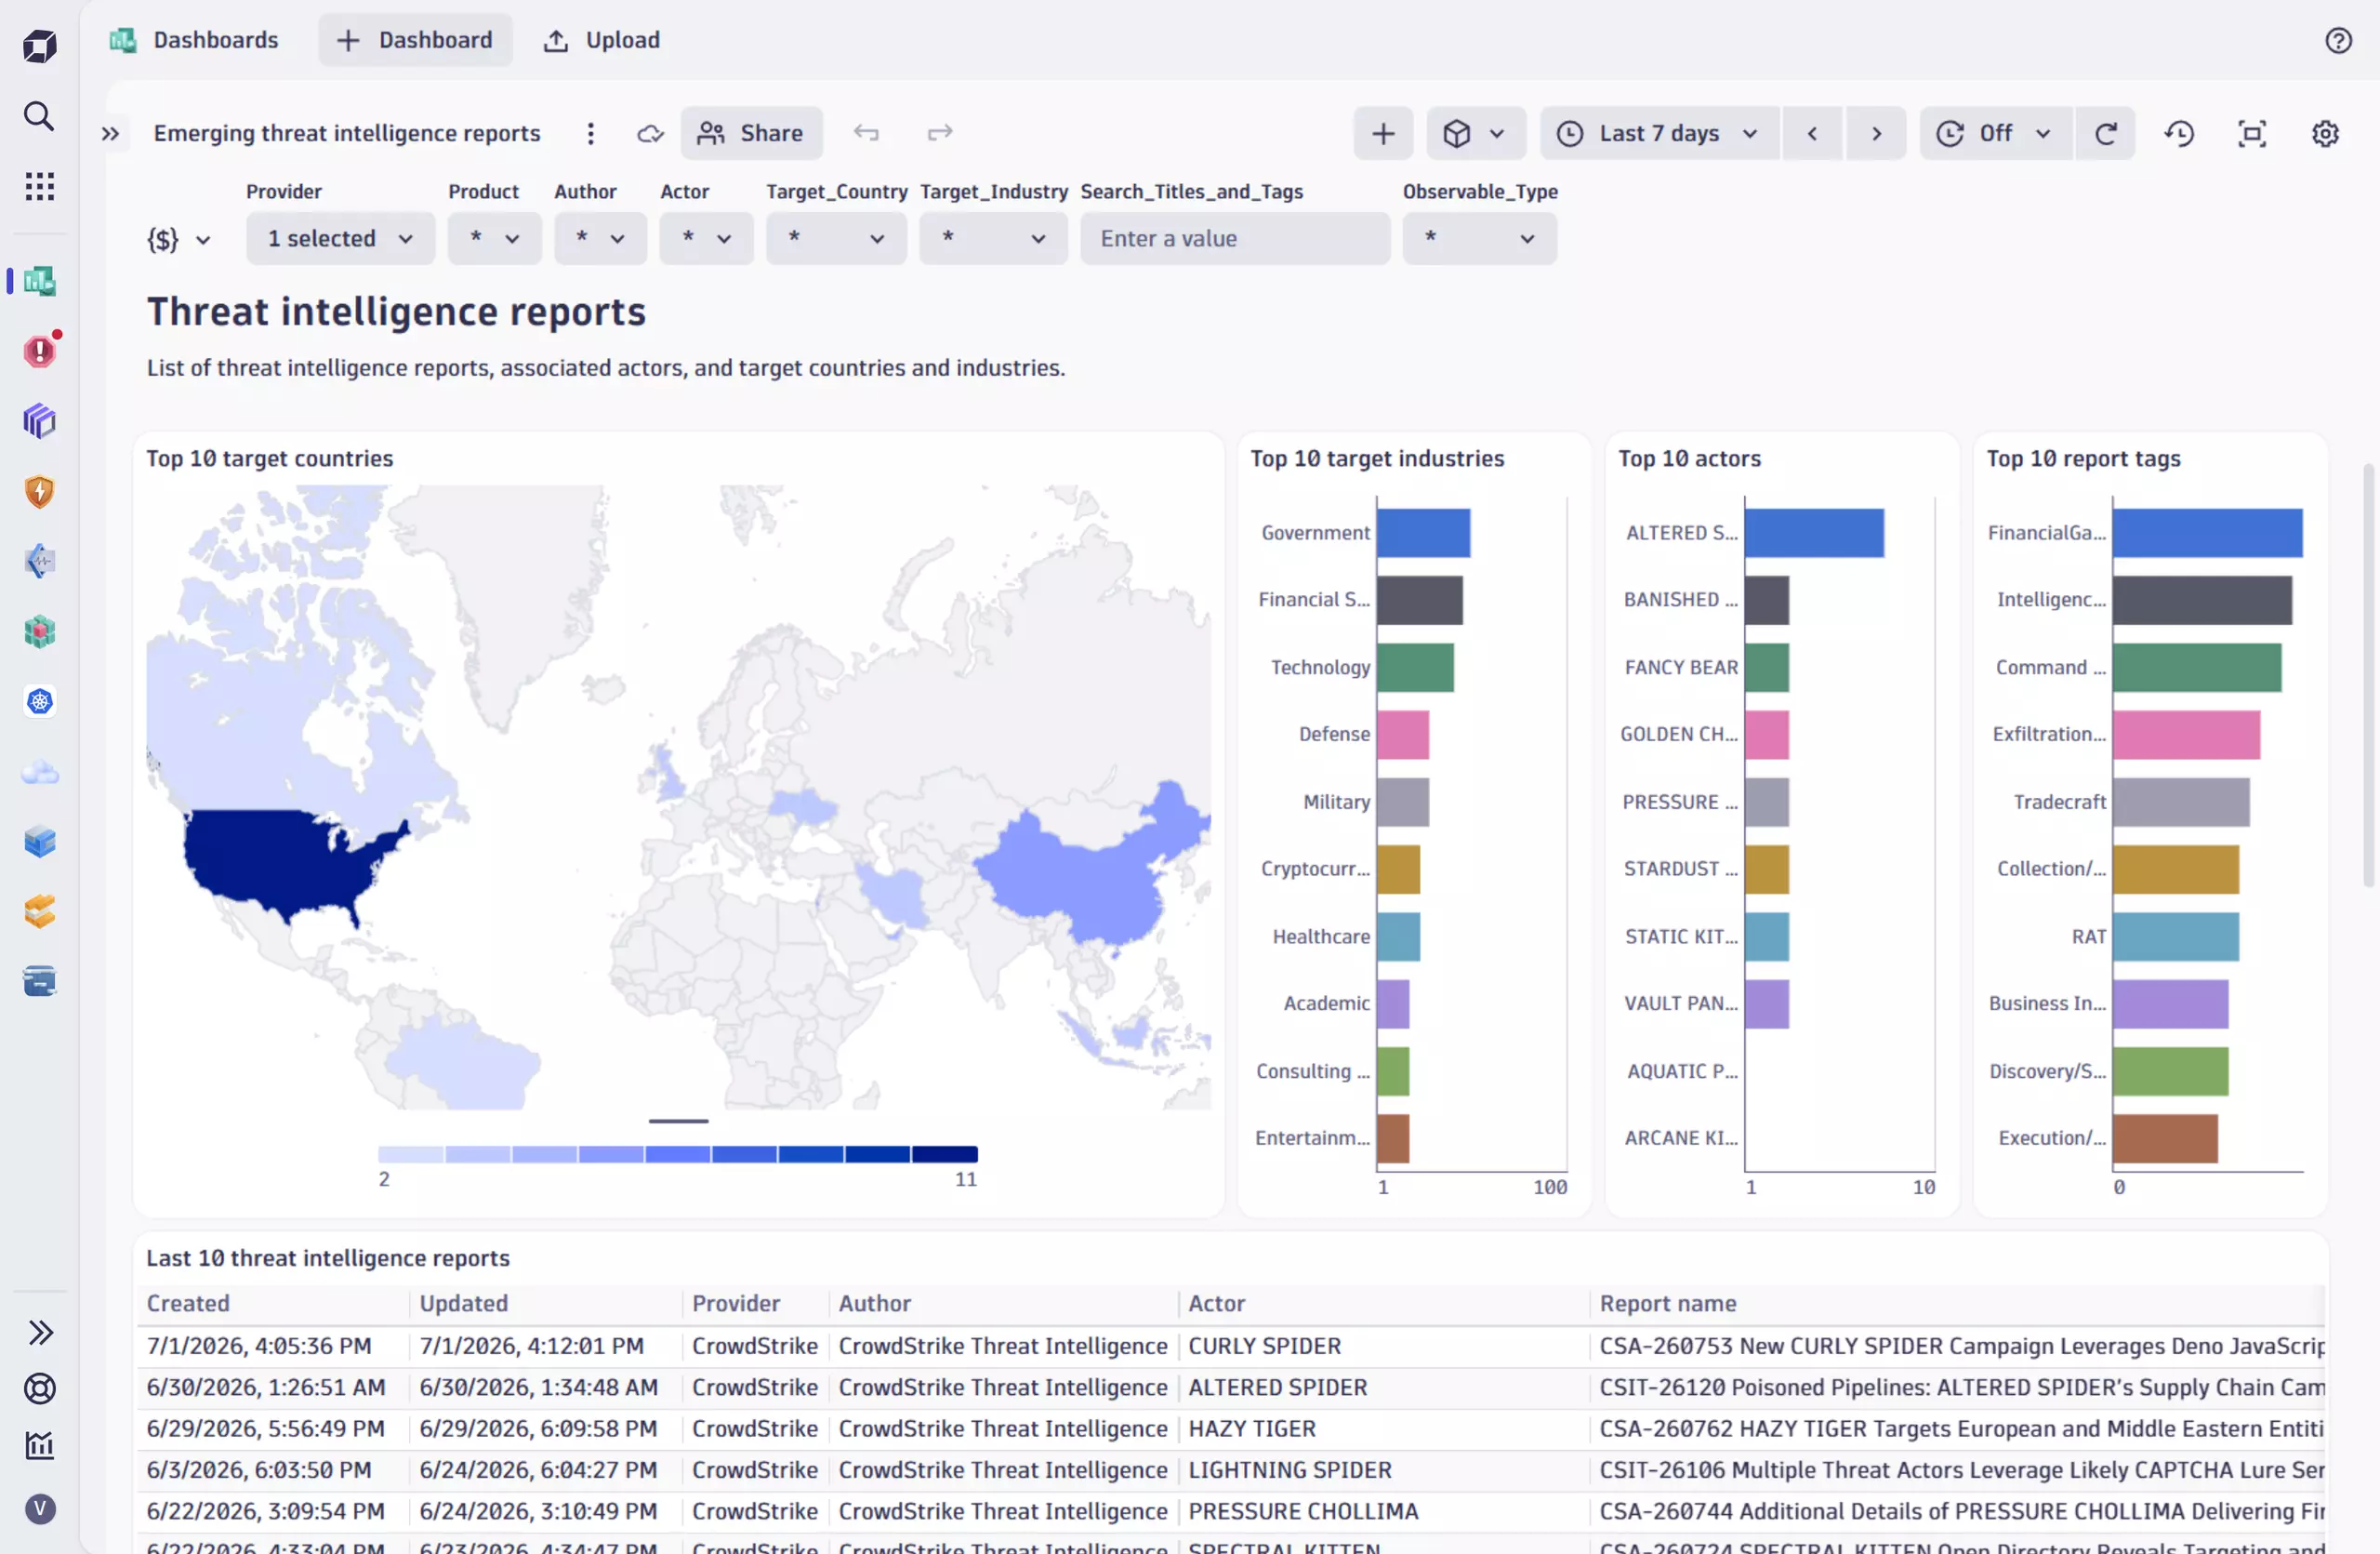
- Federated Search: Query Dynatrace data directly from CrowdStrike Falcon.
- Full-stack context: Access Dynatrace logs, metrics, traces, and topology from CrowdStrike Falcon.
- No data movement: Query Dynatrace data without ingesting another copy into CrowdStrike Falcon.
- Faster investigation: Investigate threat signals alongside logs, application, and infrastructure context.
Reduce telemetry costs with Bindplane by Dynatrace
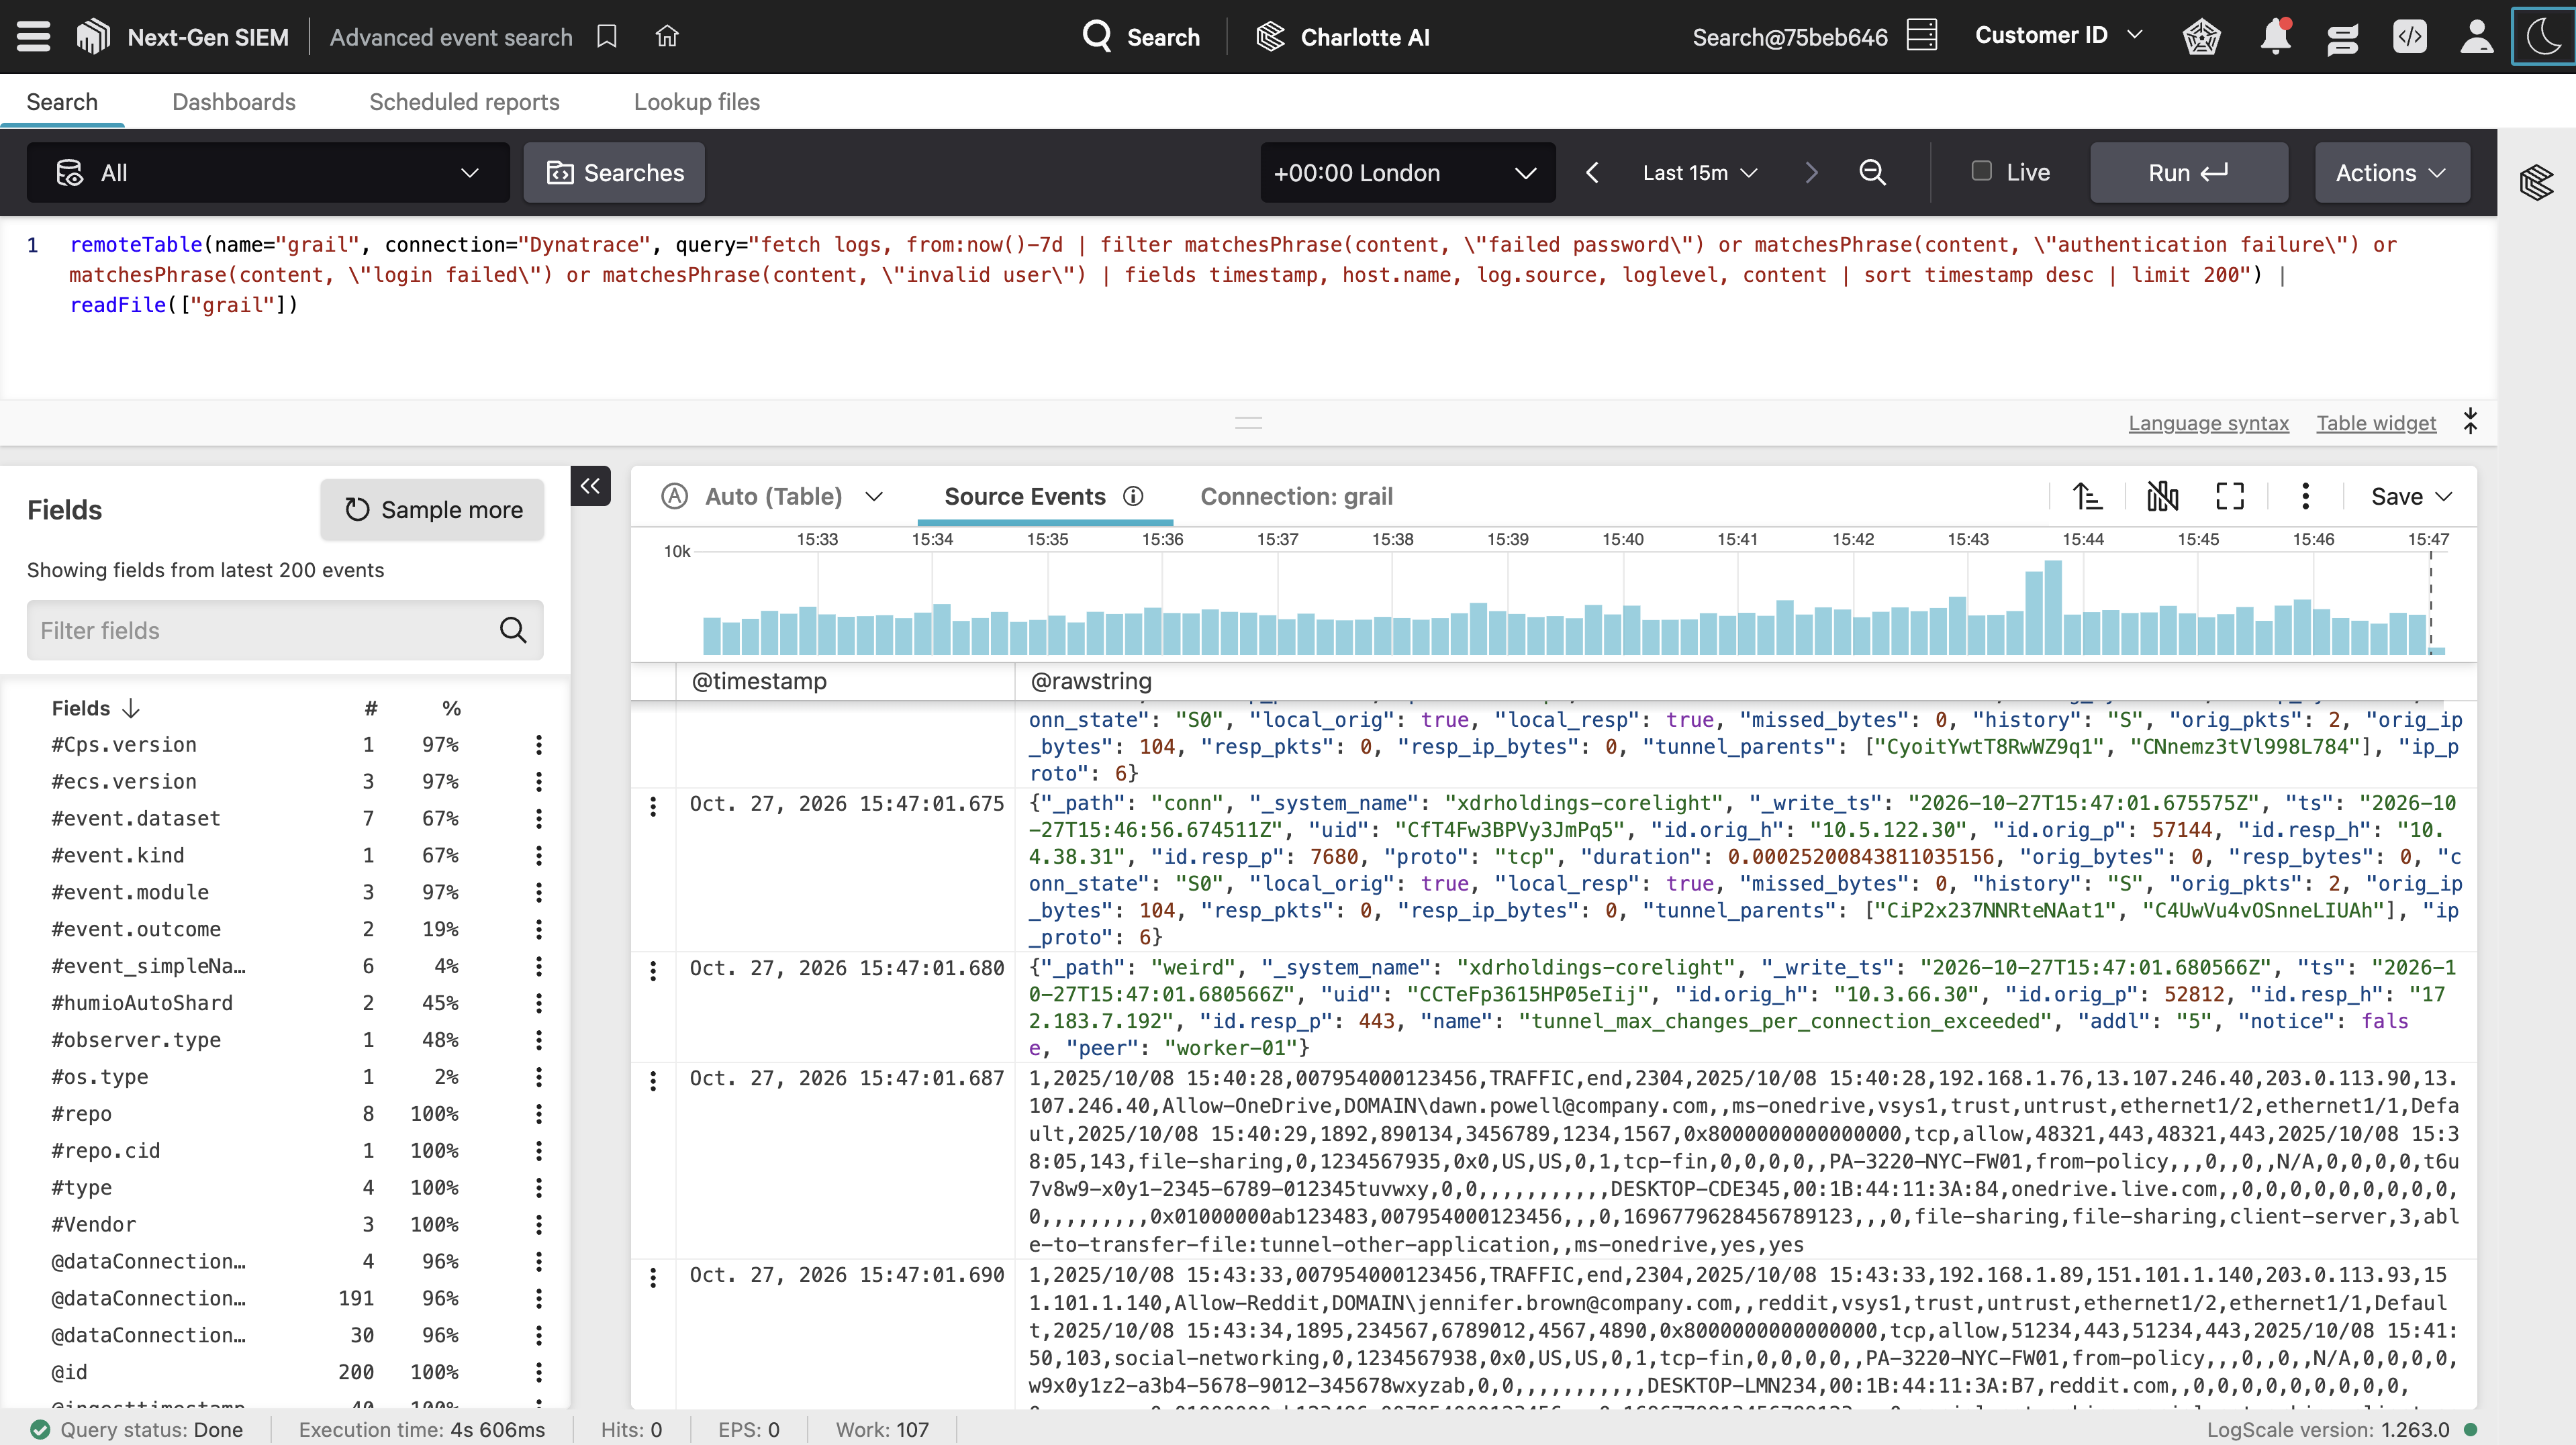
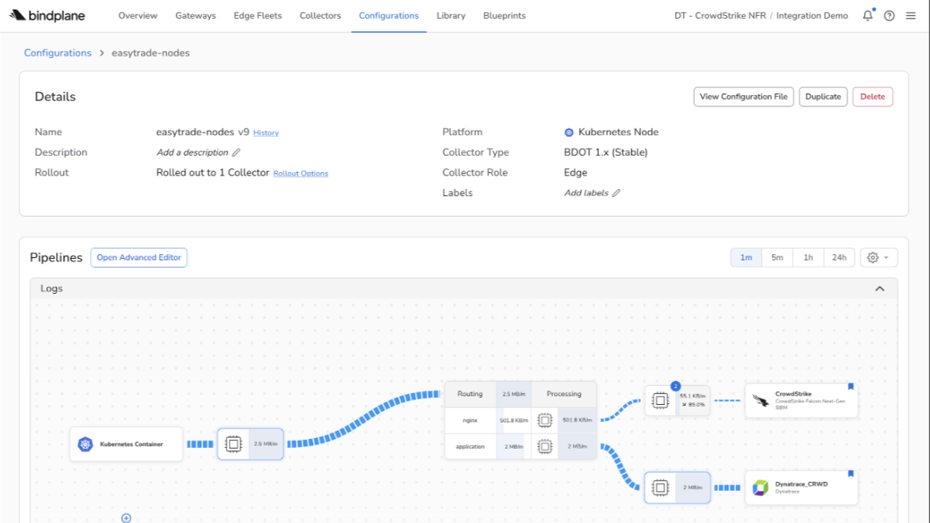
- Collect once: Collect logs and other telemetry once, then route them to Dynatrace, CrowdStrike, or both.
- Source routing: Route security and observability data before platform ingestion.
- Cost control: Reduce duplicate logs and telemetry before they reach downstream platforms.
- Flexible routing: Change log and telemetry destinations without redeploying collection agents.
See shared context in action
Before Dynatrace + CrowdStrike
A server is compromised. CrowdStrike isolates it. An SRE team sees the resulting service issue in Dynatrace but doesn’t immediately have the security context behind it. Operations and security teams must connect that information across their separate workflows to understand what happened.
With Dynatrace + CrowdStrike
With the Dynatrace integrations, CrowdStrike security data can be correlated with Dynatrace application context, helping the SRE team investigate the service impact alongside the related security activity.
Frequently asked questions
Dynatrace and CrowdStrike offer three separate integrations that connect security and observability: Falcon Insight XDR endpoint security telemetry in Dynatrace, Federated Search in Falcon Next-Gen SIEM, logs and telemetry routing via Bindplane.
The EDR integration ingests CrowdStrike endpoint security detection events into Dynatrace, enabling operations teams to correlate security alerts with logs, application topology and performance data — without switching tools.
Bindplane is a telemetry pipeline that routes logs and telemetry at the source, directing security events to the Falcon platform and performance data to Dynatrace simultaneously — eliminating duplicate ingestion and reducing operational costs.


Try it free
